In 30 seconds
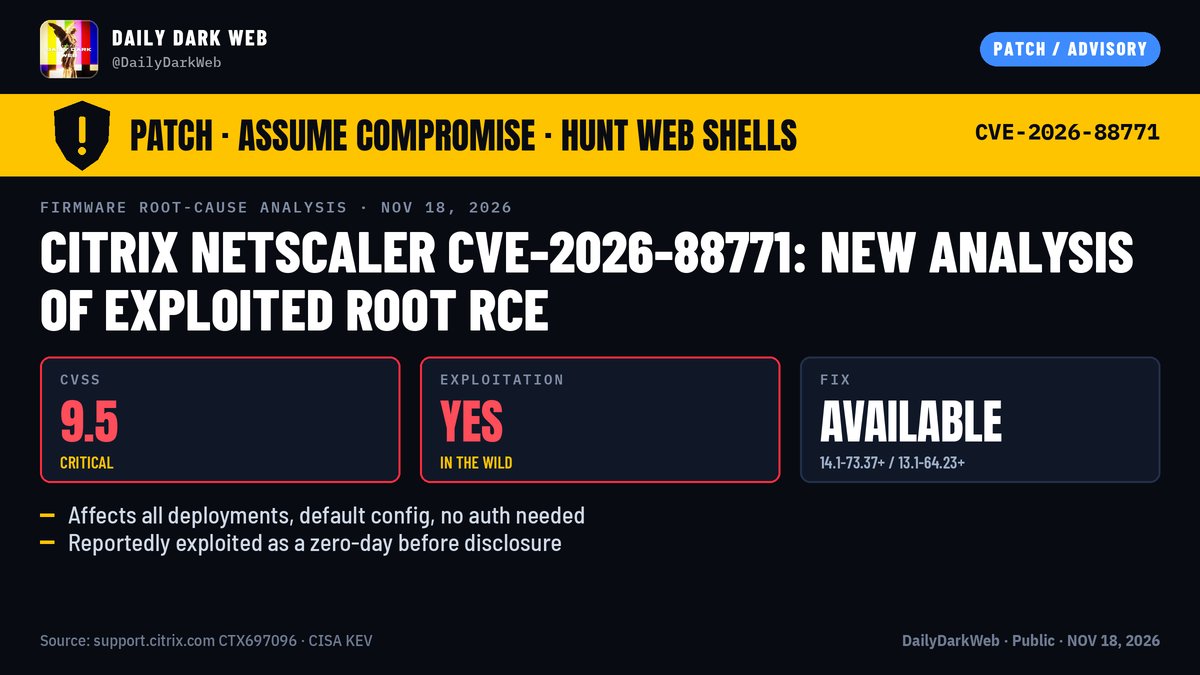
The newest turn in the Citrix NetScaler story is a public root-cause analysis, published November 18, that explains exactly how CVE-2026-88771 works. It is a critical flaw, scored 9.5 out of 10 under CVSS v4.0, in NetScaler ADC and Gateway appliances, and it lets an attacker run commands as root, the highest privilege on the box, without ever logging in.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listCitrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rssOpen original sourceSee in source list
The mechanism, as laid out in the analysis: a failed login attempt on the management interface, no credentials required, writes text the attacker controls into the appliance log. Later, a maintenance script that runs as root reads that log entry and hands the text to a shell command. The result is unauthenticated remote code execution, meaning the attacker's own commands run with full privileges on the appliance.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Exploitation is confirmed in the wild, and CISA placed the flaw on its KEV catalog, the list of vulnerabilities known to be actively exploited, on September 27, 2026. Fixes have been available since late September for every affected version, so the story today is less about the patch and more about understanding what attackers could do with the bug.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listCitrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rssOpen original sourceSee in source list
What happened
Citrix opened this chapter on September 27, 2026, with security bulletin CTX697096, covering CVE-2026-88771 through CVE-2026-88778, and listing fixed builds for every affected branch, from the mainstream 14.1 and 13.1 lines to the FIPS and NDcPP variants.Citrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rssOpen original sourceSee in source list
The same day, CISA added the flaw to its Known Exploited Vulnerabilities catalog. The bulletin's own source list shows the response stacking up quickly, with advisories from CISA, the Canadian Centre for Cyber Security and CERT-EU, plus intrusion analysis from Rapid7 and detection reports from Zscaler.Citrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Then, on November 18, the public root-cause analysis appeared and turned a patch advisory into a full explanation of the bug, describing the chain from a failed management login all the way to code execution as root.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
What makes this bug serious is its reach. All customer-managed NetScaler ADC and Gateway deployments are affected, in the default configuration, with no extra feature or special setup needed. Combine that with unauthenticated, root-level code execution and a single exposed appliance becomes a full compromise of whatever sits behind it.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listCitrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rssOpen original sourceSee in source list
The new write-up cuts both ways. It helps defenders understand what they have been patching, and it hands would-be attackers a clearer map of the terrain. The analyst note makes one more practical point worth repeating: installing the patch does not remove web shells or rogue accounts an intruder may already have planted.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
First, get to a fixed build. Citrix lists 14.1-73.37 or later and 13.1-64.23 or later as the fixed mainstream versions, with 14.1-73.37 FIPS and 13.1-37.279 or later covering the FIPS and NDcPP lines. The later 14.1-73.46 and 13.1-64.29 builds also address a separate SAML issue tracked as CVE-2026-107406.Citrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rssOpen original sourceSee in source list
Second, treat any appliance that ran an exposed vulnerable build as a potential incident, not just a config task: preserve logs, rotate credentials, and hunt for web shells and rogue accounts. Patching closes the door. It does not evict whoever already walked through it.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
Established so far: the flaw and its critical severity, the exact affected and fixed versions, the September 27 disclosure, the same-day KEV listing, and the mechanism as described by the November 18 analysis.Citrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Still open: the analysis reportedly says attackers used the flaw as a zero-day, meaning they exploited it before any patch existed, for at least two weeks before disclosure. That timing is attributed rather than documented in this batch, and nothing here identifies specific victims or confirms that any particular organization was breached.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
DailyDarkWeb, summarizing the new analysis, framed the November 18 write-up as helpful to defenders and attackers alike, and urged teams to move from a patching posture to an incident-response posture for any appliance that was exposed while vulnerable.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Citrix's own bulletin stays in classic advisory mode: enumerate the affected versions, point to the fixed builds, and cross-reference the government and vendor advisories that followed, without commenting on the root-cause analysis itself.Citrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rssOpen original sourceSee in source list
Evolution
The picture sharpened in three steps. September 27 brought the bulletin and the fixes. The same day, CISA confirmed active exploitation by listing the flaw in the KEV catalog. November 18 brought the public mechanics of the bug itself, closing the loop from patch now to here is exactly how it works.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listCitrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rssOpen original sourceSee in source list
Each step changed the defender's job. First it was patch fast, then assume exploitation attempts, and now, with the root cause public, it is understand the bug, check for leftovers, and assume attackers received the same lesson at the same moment.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 1 engagements.
Technical detail
Step by step, per the analysis: the attacker sends a failed login to the management interface, no credentials involved. The appliance writes the attacker's text into its log. A maintenance script owned by root later reads that log entry and passes the text to a shell command. Because the shell runs as root, the injected text executes with full privileges, giving unauthenticated remote code execution as root, scored 9.5 under CVSS v4.0.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Affected builds, per the Citrix bulletin: NetScaler ADC and Gateway 14.1 before 14.1-73.37, 13.1 before 13.1-64.23, 14.1-FIPS before 14.1-73.37 FIPS, and 13.1-FIPS and NDcPP before 13.1-37.279. The follow-up SAML vulnerability, CVE-2026-107406, touches 14.1 before 14.1-73.46 and 13.1 before 13.1-64.29.Citrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rssOpen original sourceSee in source list
Fixed builds: 14.1-73.37 or later and 13.1-64.23 or later for the mainstream lines, 14.1-73.46 or later and 13.1-64.29 or later to also cover the SAML issue, 14.1-73.46 FIPS, and 13.1-37.283 for the 13.1-FIPS and NDcPP tracks.Citrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rssOpen original sourceSee in source list
Sources and evidence
The primary source is Citrix's own security bulletin CTX697096, published September 27, 2026, which anchors the CVE list, the affected and fixed versions, and the disclosure timeline, and which cross-references the CISA, Canadian, CERT-EU, Rapid7 and Zscaler material.Citrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rssOpen original sourceSee in source list
The discussion source is a DailyDarkWeb post dated November 18 that summarizes the new root-cause analysis, relays the CVSS 9.5 score, the KEV date and the reported two weeks of pre-disclosure zero-day use, and adds the analyst note on incident response. The underlying analysis itself is not in this batch, so the details of the mechanism rest on this summary.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x
- Citrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778 (CTX697096)support.citrix.com · rss


