In 30 seconds
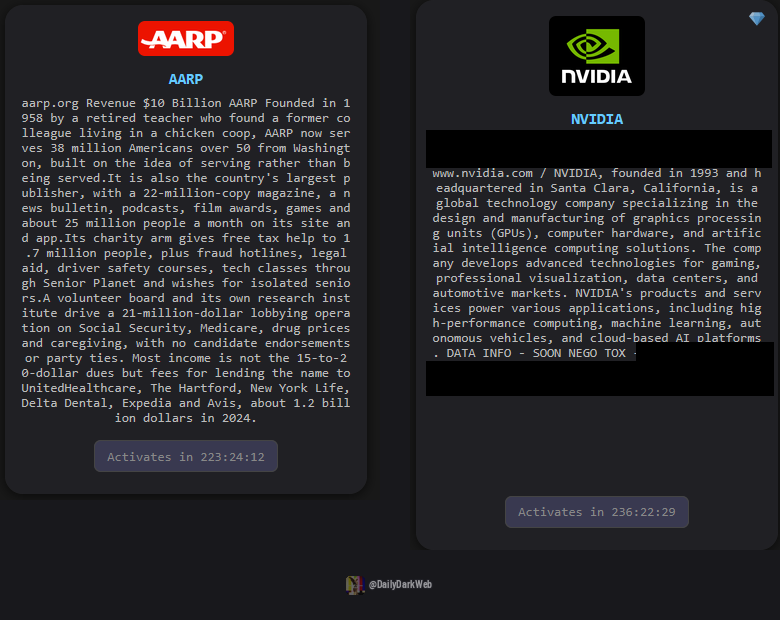
The Gentlemen ransomware crew has turned up the heat on AARP: the group's leak site, the extortion page where gangs threaten to publish data, now shows a countdown clock on the AARP entry with roughly 223 hours left as of about 4:50 PM ET on November 18, pointing to a threatened release near November 28. An NVIDIA entry on the same site shows a similar timer. Neither listing offers file samples or a list of what data is supposedly held, and DailyDarkWeb, which checked the pages, found no statement from either organization.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
This is the second extortion claim against AARP in three days, after a separate group called N0n named the organization on November 16. Everything here rests on what the groups themselves posted. Nothing confirms that any data was actually taken from AARP.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
The Gentlemen added AARP, aarp.org, to its leak site on November 17, 2026. The entry names AARP as the victim, describes it as a US membership organization with insurance partnerships, and spends most of its space profiling AARP's licensing business with UnitedHealthcare and other partners. As first posted, it gave no data volume, no file samples and no ransom deadline.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Roughly a day later the pages changed. The AARP entry picked up an 'Activates in' countdown of about 223 hours and NVIDIA's entry one of about 236 hours, both pointing to a date around November 28. NVIDIA's data section still reads 'DATA INFO - SOON' and lists a contact for 'negotiation', which DailyDarkWeb reads as a sign that talks may be pending.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The claim did not appear out of nowhere. On November 16 the data extortion group N0n had already named AARP in a batch that also listed Airbnb and Nielsen. No statement from AARP has surfaced for either listing, and neither claim has been independently verified.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
AARP is not a small target. It is the Washington, DC-based nonprofit that represents about 38 million Americans aged 50 and over, and its business includes licensing arrangements with UnitedHealthcare and other partners. Data tied to an organization like this sits at the intersection of personal details and health insurance, a sensitive mix.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The audience matters as much as the data. As DailyDarkWeb notes, older Americans are heavily targeted by fraud and phishing, so any genuinely stolen data could be repurposed quickly into scams aimed at a population already under siege.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Two groups naming the same victim within three days raises its own questions. Possible explanations include a shared access broker, meaning a middleman who sells network entry to gangs, recycled data from an earlier incident, or an opportunistic re-listing meant to make the group look powerful. For now all of it stays hypothesis.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
Treat the countdown as theater until proven otherwise. As DailyDarkWeb puts it, a timer is pressure the group sets for its victim, not proof that data was stolen. The concrete things to watch before the clocks run out near November 28 are data samples appearing on the leak site or a statement from AARP.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
For AARP members, nothing is confirmed, so there is no breach-specific action to take. Given how heavily this demographic is targeted by phishing, the sensible posture is the usual one: be wary of unexpected calls or emails that cite the incident or rush you into acting.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
What is established so far: The Gentlemen runs a leak-site entry for AARP, posted November 17, with a countdown pointing to about November 28, and a parallel NVIDIA entry shows the same pattern. No file samples or data lists have appeared, and neither AARP nor NVIDIA has said anything publicly as of the November 18 check.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What is not: whether any AARP data was taken at all, how much, or of what kind. Whether negotiations are happening behind the scenes, which the 'negotiation' contact hints at but cannot confirm. And why two separate groups, The Gentlemen and N0n, claim the same victim within three days.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
The only voice in this batch is DailyDarkWeb, a threat intelligence account that reported both listings and attached an explicit warning: this is an unverified ransomware group claim, not confirmation of a breach. On the other side, the group's own page speaks through its text, including 'DATA INFO - SOON' and a negotiation contact on the NVIDIA entry. AARP and NVIDIA have said nothing that DailyDarkWeb could find.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The timeline is short and escalating. November 16: N0n names AARP in a batch alongside Airbnb and Nielsen. November 17: The Gentlemen adds its own AARP listing, profiling the UnitedHealthcare licensing business, with no deadline and no samples. November 18: countdown timers appear on the AARP and NVIDIA entries, about 223 and 236 hours respectively, pointing to a threatened release around November 28. In two days the pressure moved from a bare name on a page to a public clock.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 3 updates, and 28 engagements.
Technical detail
Mechanically this is standard leak-site extortion. The gang posts a victim page, then adds an 'Activates in' timer, here about 223 hours for AARP and about 236 for NVIDIA, both landing near November 28. NVIDIA's page still says 'DATA INFO - SOON' and lists a contact for 'negotiation', the channel through which a victim would bargain before the timer expires.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
DailyDarkWeb adds a caution rooted in the group's track record: The Gentlemen has a history of listing victims without evidence. That is the account's characterization, offered as an analyst note, and it is one more reason to hold judgment.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
The entire evidence base is two posts from DailyDarkWeb: one from November 17 reporting the AARP listing and the earlier N0n claim, and one from November 18 reporting the countdown timers on the AARP and NVIDIA entries. Both are descriptions and screenshots of a criminal leak site, a page the actor itself controls. This batch contains no victim statement, no regulator filing, no sample data and no third-party confirmation.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x
- DailyDarkWebx.com · DailyDarkWeb · x


