In 30 seconds
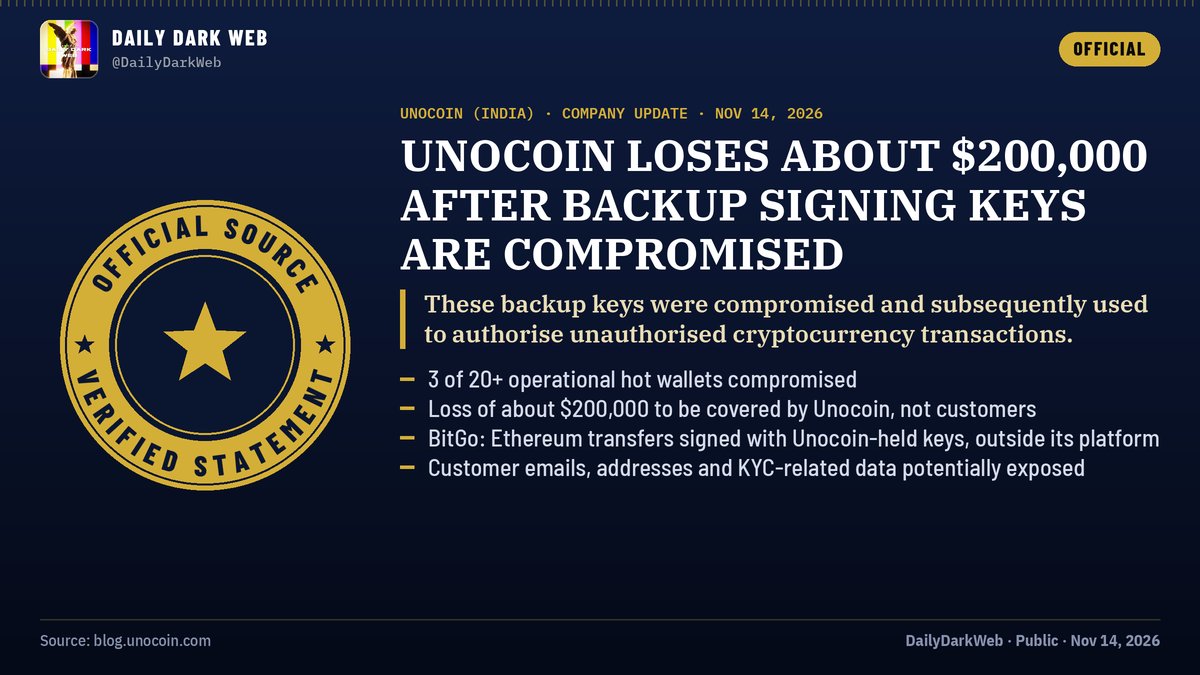
Crypto exchange Unocoin now puts its losses at about $200,000 after, by its own account, someone compromised its backup signing keys, the spare cryptographic credentials that can authorize transactions. The exchange says those keys were then used in Ethereum transfers.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
BitGo says the Ethereum transfers it reviewed were signed with keys Unocoin held itself, outside BitGo's platform. That placement is the crux of the whole incident.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The practical upshot: once self-custody keys, the kind the customer controls directly, are stolen, freezing the platform does nothing. The blockchain accepts any transaction carrying a valid signature, no matter who made it.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
Unocoin broke the news in a security incident update published on its blog. In it, the exchange reports that its backup signing keys were compromised and puts the resulting losses at roughly $200,000.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source list
Ethereum transfers signed with those keys followed. BitGo, after reviewing them, says the signatures came from keys Unocoin held outside BitGo's platform.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listblog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source list
That placement explains the aftermath. Freezing activity on a platform only blocks what the platform controls, and these signatures came from keys it did not control.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
Backup keys are the quiet risk in this story. They exist so a company can recover access, but whoever holds them can sign away funds just as effectively as the owner, and no exchange-side emergency stop can revoke that power.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source list
The incident also sketches the boundary of custody. Even with a custodian in the picture, keys a customer keeps for itself sit outside the custodian's protective perimeter; when those are taken, the custodian can observe and attest, as BitGo did here, but not block.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
For operators, the lesson is to treat backup signing keys as the funds themselves: keep them offline, split access so no single copy can act alone, and rotate them the moment compromise is suspected. After the fact there is no freeze to fall back on.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
For users, nothing actionable appears in the evidence yet: no word on affected accounts, reimbursements, or a claims process. Unocoin's official channels are the place to watch, rather than screenshots circulating elsewhere.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source list
Confirmed and still uncertain
What is established so far is mostly what the parties claim: Unocoin's own accounting of about $200,000 in losses, its report that backup signing keys were compromised, and BitGo's finding that the reviewed transfers used Unocoin-held keys outside its platform.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What is not established: who took the keys, how they got them, whether the losses are final or still growing, and whether any moved funds can be traced or recovered. The blog update's full text is also thin in this batch, so some detail rests on a summary from a third party.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
Unocoin, through its security incident update, is the source of the $200,000 figure and of the account that its backup signing keys were compromised and used in Ethereum transfers.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source list
BitGo has kept its statement narrow: the Ethereum transfers it reviewed were signed with keys Unocoin held, not keys on BitGo's platform.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
DailyDarkWeb, an account that surfaces breach news, amplified the update with a screenshot and distilled the takeaway: a platform freeze cannot stop transfers signed with stolen self-custody keys.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The story opened with Unocoin's incident update: backup signing keys compromised, losses near $200,000, Ethereum transfers in the mix.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source list
BitGo's review then sharpened the picture. By placing the compromised keys outside its platform, it explained why the usual emergency measure, freezing, was never going to hold back these transfers.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 3 engagements.
Technical detail
A signing key is the private half of a cryptographic pair; whoever holds it can produce the signature that makes an Ethereum transfer valid. Backup signing keys are spare copies kept for recovery, and that is exactly why they are dangerous in the wrong hands: they carry the same authority as the originals.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source list
The custody split is the technical crux. Keys held inside a platform can be frozen there, but keys held outside, which is where BitGo says these were, answer only to whoever possesses them. The blockchain checks signatures, not permission slips.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listblog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source list
Sources and evidence
This report rests on two items: Unocoin's security incident update on its official blog, the primary source, and a post from DailyDarkWeb that summarizes it and carries the BitGo statement.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
One caveat deserves flagging: the blog item's full text was not captured in this batch, so the loss figure, the key compromise, and BitGo's exact wording all arrive through attribution rather than verbatim text. Treat them as claims, well sourced but not independently verified here.blog.unocoin.comblog.unocoin.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- blog.unocoin.comblog.unocoin.com · rss
- DailyDarkWebx.com · DailyDarkWeb · x


