In 30 seconds
A poisoned Quantum Systems update reportedly reached German military servers, but not the drones themselves. Quantum says its aircraft remain operational, while Germany's military reportedly grounded its drones as a precaution.IntCyberDigestx.com · IntCyberDigest · xOpen original sourceSee in source list
What happened
The incident reportedly began in late October, when hackers planted malware on servers belonging to German drone maker Quantum Systems. The alleged plan was to deliver it through the company's update process so that installed drones would become unusable, at least temporarily.IntCyberDigestx.com · IntCyberDigest · xOpen original sourceSee in source list
Why it matters
If the account is accurate, the incident shows how compromising a manufacturer's update infrastructure could create a path toward military systems without directly attacking each drone. Reaching military servers also matters even when the payload never reaches the aircraft, because it exposes a trusted distribution channel to possible manipulation.IntCyberDigestx.com · IntCyberDigest · xOpen original sourceSee in source list
What to do
Quantum Systems and affected military operators should preserve logs, identify every server that received the update, verify whether it executed, rotate exposed credentials and independently validate future packages before deployment. The evidence provided does not show whether those steps have already been completed.IntCyberDigestx.com · IntCyberDigest · xOpen original sourceSee in source list
Confirmed and still uncertain
The available item says the update reached German military servers but stopped before the drones. It does not provide the malware's name, technical indicators, affected server count, entry method, forensic findings or direct evidence identifying the attackers.IntCyberDigestx.com · IntCyberDigest · xOpen original sourceSee in source list
What people are saying
The post says security sources told German broadcaster BR that much of the evidence points toward Russia, while Der Spiegel reportedly described the update reaching German military servers. Quantum Systems, meanwhile, says its drones are flying normally, countering any implication that the fleet was successfully disabled.IntCyberDigestx.com · IntCyberDigest · xOpen original sourceSee in source list
Evolution
The reported sequence starts with malware being planted on Quantum Systems servers in late October. A compromised update then allegedly reached German military servers but not the aircraft, after which Germany's military grounded its drones as a precaution while Quantum said they remained operational.IntCyberDigestx.com · IntCyberDigest · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 4 engagements.
Technical detail
The described method resembles a software supply-chain attack: malware is inserted into a vendor-controlled update and travels through a channel customers normally trust. In this account, the intended final effect was temporary loss of drone usability, although no payload analysis is supplied to verify that capability.IntCyberDigestx.com · IntCyberDigest · xOpen original sourceSee in source list
Sources and evidence
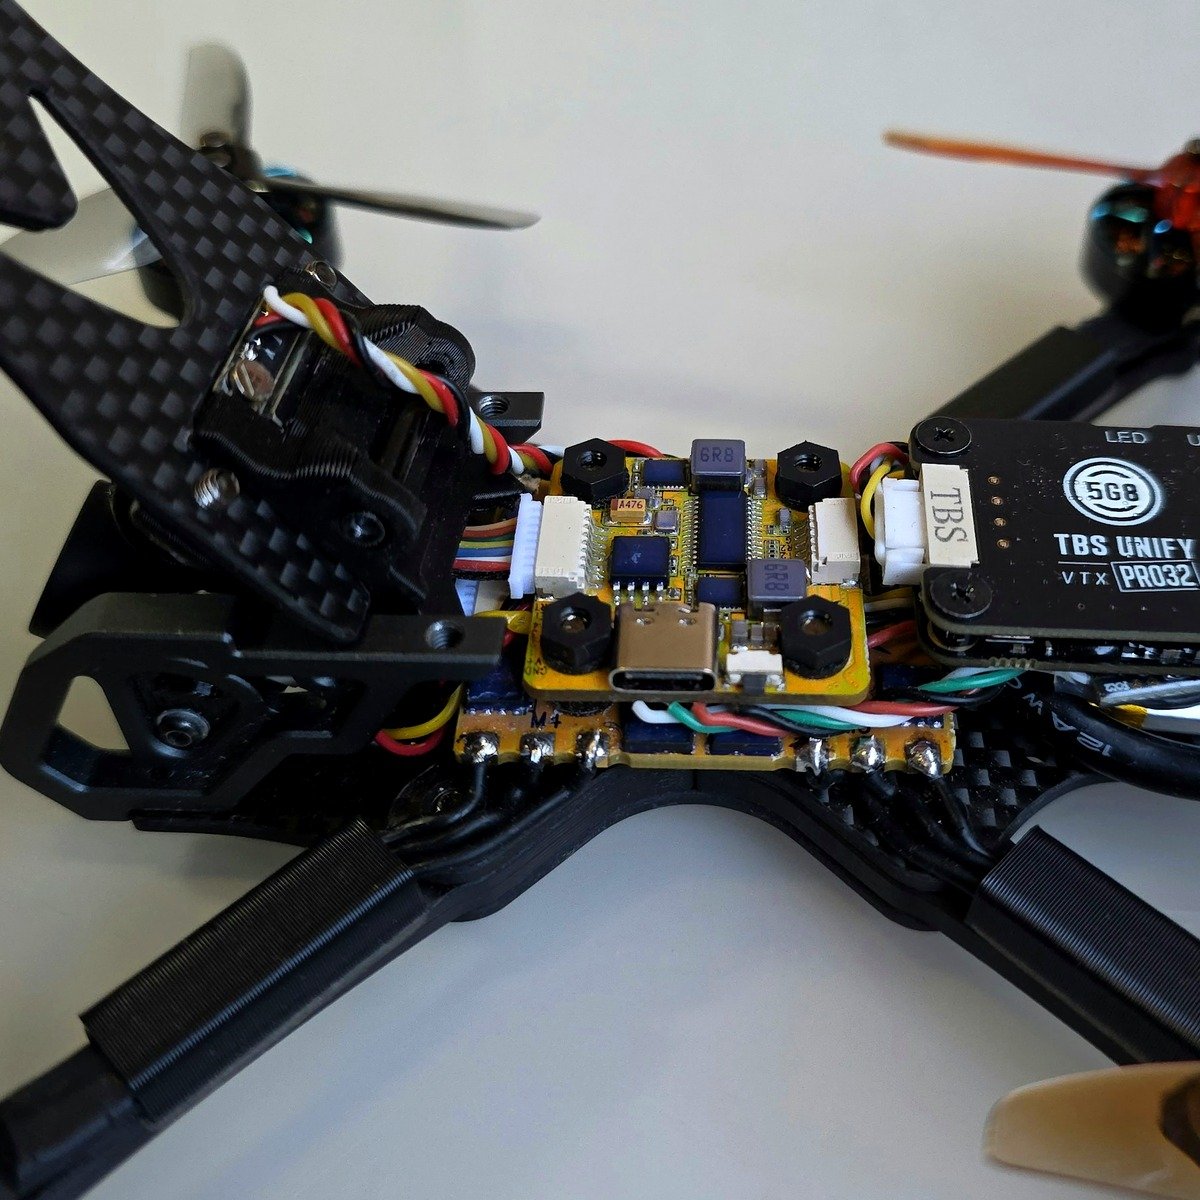
The evidence lot contains one X post that summarizes reporting attributed to BR and Der Spiegel and includes an image. It provides no linked primary report, official incident notice, forensic artifact or named security source, so the intrusion, motive, attribution and operational impact remain unverified within this lot.IntCyberDigestx.com · IntCyberDigest · xOpen original sourceSee in source list
Sources
- IntCyberDigestx.com · IntCyberDigest · x