In 30 seconds
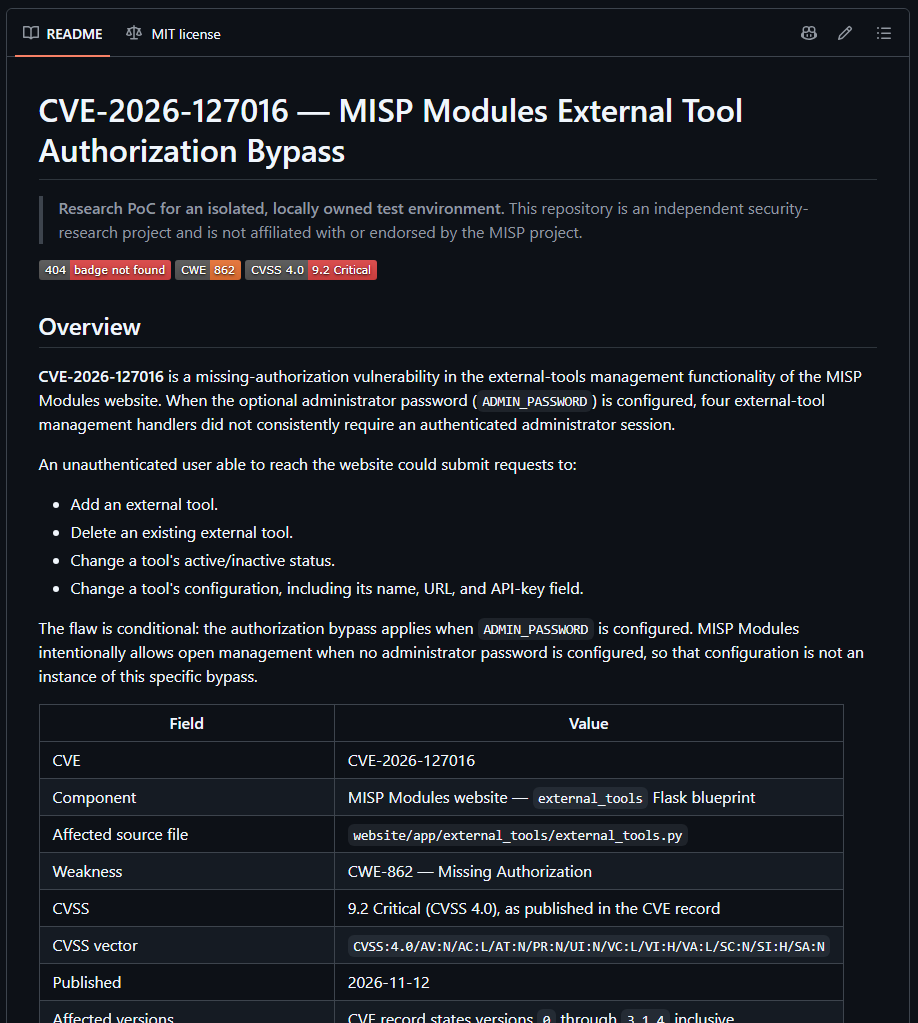
The latest evidence links a public GitHub repository presented as a proof of concept for CVE-2026-127016. A social post alleges that network-reachable MISP Modules deployments through version 3.1.4 can let unauthenticated attackers change external-tool configurations when administrator authentication is configured but not enforced by the relevant endpoints.github.comgithub.com · rssOpen original sourceSee in source listDarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
What happened
DarkWebInformer says the MISP Modules website component has external-tool management endpoints that fail to enforce the configured administrator authentication policy. The reported actions include adding or removing tools, enabling or disabling them, and changing API keys or ingestion URLs without authentication.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Why it matters
If the reported behavior is reproducible, changing keys, tool status, or ingestion destinations could disrupt integrations or alter how external tools authenticate and where they send data. The evidence supports this as a plausible consequence, not as proof that any deployment has been compromised.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
What to do
Administrators should limit network access to the management interface and review the configured tool list, activation states, API keys, and ingestion URLs for unexpected changes. Because the supplied evidence names no fixed release, these are precautionary measures rather than a substitute for vendor remediation.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Confirmed and still uncertain
The supplied batch shows a GitHub repository dedicated to the CVE and a post describing its alleged impact. It does not provide repository contents, a vendor advisory, a patched version, independent reproduction results, or evidence of exploitation in the wild.github.comgithub.com · rssOpen original sourceSee in source listDarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
What people are saying
DarkWebInformer characterizes the issue as CWE-862, Missing Authorization, assigns it a CVSS score of 9.2, and calls it critical. The post identifies MISP Modules versions through 3.1.4 as affected, but the batch contains no independent source confirming that assessment.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Evolution
The GitHub repository and the social post carry the same recorded publication time, with the post directing readers to the repository as the PoC. No later update, vendor response, or remediation notice appears in the supplied evidence.github.comgithub.com · rssOpen original sourceSee in source listDarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 9 engagements.
Technical detail
The reported attack path is direct access to external-tool management endpoints without valid administrator authentication. Those endpoints allegedly accept operations that create or delete tools, toggle their status, and rewrite sensitive settings, including API credentials and ingestion destinations.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Sources and evidence
The GitHub item establishes the existence of a repository named for CVE-2026-127016, but its supplied record contains no title or body. All substantive claims about affected versions, severity, conditions, and impact come from the DarkWebInformer post, so the technical account remains singly sourced within this batch.github.comgithub.com · rssOpen original sourceSee in source listDarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Sources
- github.comgithub.com · rss
- DarkWebInformerx.com · DarkWebInformer · x