In 30 seconds
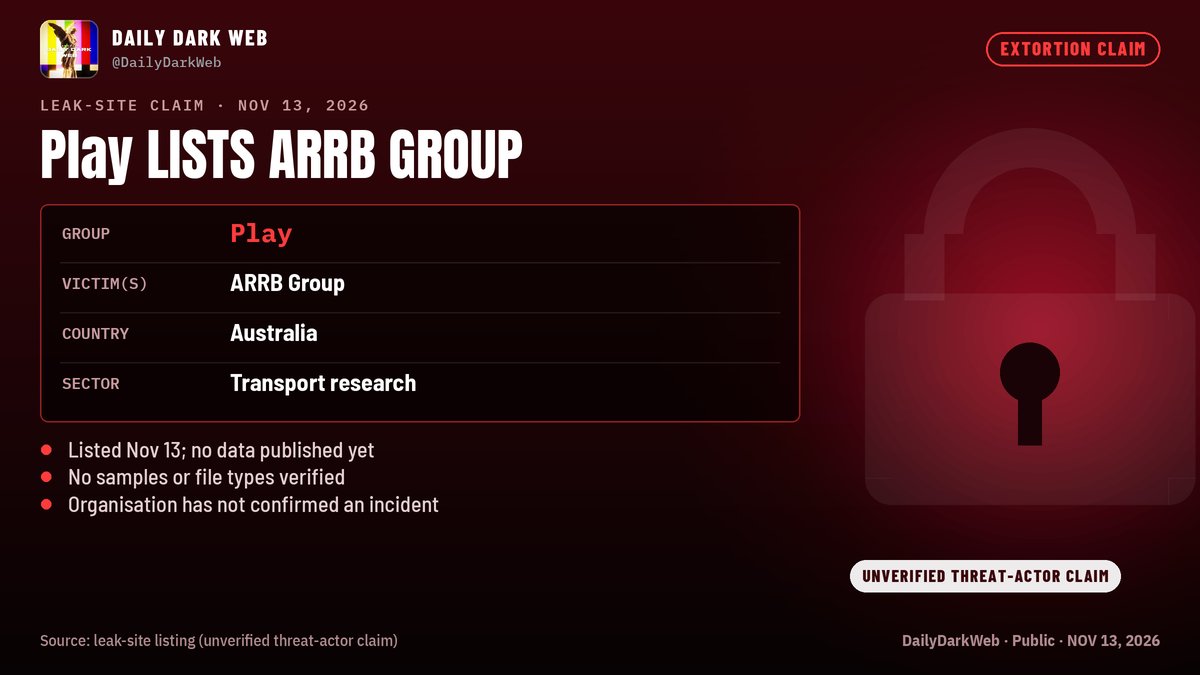
On November 13, 2026, DailyDarkWeb reported that the PLAY ransomware group had listed Australian transport research organization ARRB Group on its leak site. The post says the listing contains no data samples or other details, and the claim remains unverified.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
According to DailyDarkWeb, PLAY added ARRB Group, formerly known as the Australian Road Research Board, to its leak site. No evidence in the supplied material independently establishes that ARRB systems were compromised or that information was stolen.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
DailyDarkWeb notes that a transport research organization may hold road-network information, engineering reports and contract files for public-sector clients. That describes potential exposure, not the confirmed contents of ARRB's systems or proof that PLAY obtained any files.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
Organizations connected to ARRB should treat the listing as an unverified warning and watch for ARRB-themed phishing, as DailyDarkWeb advises. Any defensive response should avoid assuming that a breach or data theft has already been established.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
What is observed is a DailyDarkWeb post describing a purported PLAY leak-site entry dated November 13. What remains unknown includes whether ARRB was compromised, whether files were taken, what data might be involved and whether the listing is authentic.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
DailyDarkWeb explicitly characterizes the entry as an unverified threat-actor claim rather than confirmation of a breach. It also says ARRB Group had not publicly confirmed an incident when the post was published.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The supplied evidence records only one stage in the story: the alleged listing appeared on November 13, 2026, without samples or technical particulars. There is no later response from ARRB, independent verification or evidence of subsequent publication in the provided material.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 0 engagements.
Technical detail
The reported listing provides no data volume, file types or samples. The evidence also contains no indicators of compromise, entry method, affected systems, encryption details or on-chain activity that could support technical attribution or validation.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
The evidence consists of one November 13 post from DailyDarkWeb, accompanied by an image and a link to the original X status. It is a secondary report of an alleged leak-site listing, not a statement from ARRB, a forensic report or independent confirmation of a breach.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x


