In 30 seconds
Peapods Finance, a decentralized finance protocol tied to the PEAS token, has reportedly been hit for around $1 million. The figure and the full story come from on-chain investigator osint_based, who posted the case on X on November 19, 2026: the attacker allegedly set a minter, the privilege that lets a wallet create new tokens from nothing, on the L2 versions of the PEAS contracts, then minted fresh tokens, bridged them to Ethereum mainnet and sold.osint_basedx.com · osint_based · xOpen original sourceSee in source list
The same post follows the money to the end. Proceeds reportedly moved on as ETH across several wallets and, in the investigator's telling, all of it landed in Tornado Cash, a mixer designed to break the trail of funds, through 22 transactions. Ten minutes before the attack, the wallet behind it was reportedly funded via a swap service that skips identity checks.osint_basedx.com · osint_based · xOpen original sourceSee in source list
What happened
The origin, as reported, sits on an L2, one of the faster and cheaper networks that run alongside Ethereum. There the attacker managed to enable a minter on the PEAS contracts, which is functionally a license to print tokens, and used it to mint PEAS the protocol never intended to exist.osint_basedx.com · osint_based · xOpen original sourceSee in source list
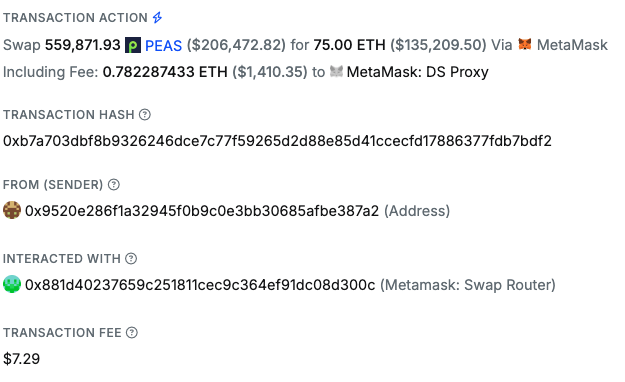
Next came the bridge, the service that carries tokens from the L2 up to Ethereum mainnet where the deeper markets sit. Once across, the minted PEAS were sold. Liquidity was thin, meaning only a small pool of money backed the price, so every swap returned far less than the tokens were nominally worth, and the selling itself pushed the price down.osint_basedx.com · osint_based · xOpen original sourceSee in source list
Then the cleanup. Per the same account, the proceeds moved as ETH through several wallets before ending in Tornado Cash in 22 transactions. The wallet at the center of it had been funded from a non-KYC swap service ten minutes before the attack started, which leaves few identity clues at the source.osint_basedx.com · osint_based · xOpen original sourceSee in source list
Why it matters
If the reporting holds, this is a supply integrity failure rather than a drained vault. Whoever controls a minter can dilute every holder at will, and the damage here landed on the PEAS price, which the reported selling pushed down, plus on the thin pools that absorbed those sales.osint_basedx.com · osint_based · xOpen original sourceSee in source list
The broader lesson is the playbook. An anonymous wallet funded minutes before the action, proceeds split across several addresses, and a finish inside a mixer is the standard route from breach to hard-to-trace cash. It is why incidents like this rarely end in recovery, though the current evidence says nothing about that either way.osint_basedx.com · osint_based · xOpen original sourceSee in source list
What to do
If you hold PEAS or provide liquidity in Peapods pools, treat this as an active incident and verify before acting. Look for a statement from the protocol's official channels, since none appears in the evidence here, and watch for fake 'support' accounts that follow incidents like this. In a thin-liquidity token, panic selling carries its own cost.osint_basedx.com · osint_based · xOpen original sourceSee in source list
For anyone monitoring rather than holding, the address flagged in the report, 0x9520e286f1a32945f0b9c0e3bb30685afbe387a2, belongs in watchlists rather than in any direct interaction.osint_basedx.com · osint_based · xOpen original sourceSee in source list
Confirmed and still uncertain
Claimed, with a traced trail attached: a minter enabled on the L2 contracts, tokens minted, bridged and sold, ETH moved across several wallets, a Tornado Cash endpoint reached in 22 transactions, and an attacker wallet funded from a no-KYC swap ten minutes before it all began.osint_basedx.com · osint_based · xOpen original sourceSee in source list
Still open is everything that matters most. The batch says nothing about how the minter got set, whether through a leaked key, a misconfigured admin function or an insider. There is no confirmation from the Peapods team, no second independent tracing, no firm loss accounting beyond the roughly $1 million estimate, and no attribution for the wallet.osint_basedx.com · osint_based · xOpen original sourceSee in source list
What people are saying
The only voice in this evidence batch is the X account osint_based, which laid out the case in an urgent post marked with warning emojis and illustrated with a screenshot of the fund flow. It presents the mint, bridge, sale and mixing chain as settled on-chain facts and puts the damage near a million dollars. No statement from Peapods Finance, and no other researcher's take, appears alongside it.osint_basedx.com · osint_based · xOpen original sourceSee in source list
Evolution
The public record here begins and ends with one post, published on November 19, 2026. By the time it appeared, every step it describes, from the minter to the final mixing transactions, was already over and presented as a finished case.osint_basedx.com · osint_based · xOpen original sourceSee in source list
That framing implies the incident surfaced publicly only after the money had moved, which is typical when analysts catch the aftermath instead of the attack in progress. With no earlier alert and no follow-up in the batch, this story is a single snapshot rather than a developing arc.osint_basedx.com · osint_based · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 1 engagements.
Technical detail
The core of the reported exploit is a minting privilege on the L2 deployments of the PEAS contracts. With a minter set, per the account, the attacker created PEAS at will and bridged the tokens to Ethereum mainnet, where the tradable liquidity sits. Thin liquidity meant each sale returned far less than the tokens' face value, and the selling itself pushed the price down.osint_basedx.com · osint_based · xOpen original sourceSee in source list
On the trail side, the post reports ETH moving through several wallets before landing in Tornado Cash across 22 transactions. The wallet tagged as the attacker's, 0x9520e286f1a32945f0b9c0e3bb30685afbe387a2, was funded from a non-KYC swap service ten minutes before the attack.osint_basedx.com · osint_based · xOpen original sourceSee in source list
Sources and evidence
This item rests on a single source: an X post by the account osint_based, published on November 19, 2026, with the full narrative plus one screenshot of the fund flow. The wallet address, the transaction count and the timeline all trace back to that one post.osint_basedx.com · osint_based · xOpen original sourceSee in source list
The caveat writes itself. One tracking account, however careful, is still one account, and the mechanics in on-chain reports tend to be more reliable than the interpretations around them. How the compromise happened, the final loss figure and any attribution all await a second tracing or an official word from Peapods. Until then, everything above reads as one researcher's account of the chain.osint_basedx.com · osint_based · xOpen original sourceSee in source list
Sources
- osint_basedx.com · osint_based · x