In 30 seconds
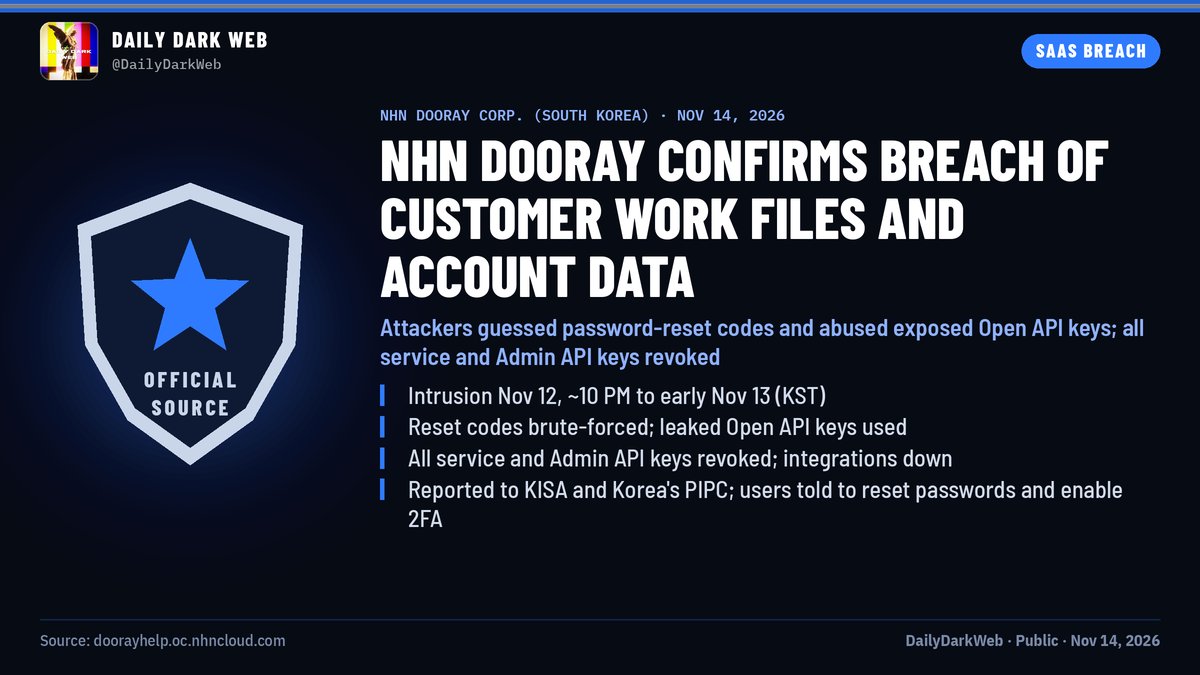
NHN, the South Korean company behind the Dooray workplace suite, has reportedly confirmed a leak of customer work files and account data. According to DailyDarkWeb's summary of the company's official notice, the intruders got in two ways: they guessed the short codes used to approve password resets, and they used API keys, the credential strings that let software connect to a service, which had been left exposed. NHN's response was blunt. It revoked every service and Admin API key, which also broke the integrations customers had built on them.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listdoorayhelp.oc.nhncloud.comdoorayhelp.oc.nhncloud.com · rssOpen original sourceSee in source list
What happened
The primary document is a notice published on Dooray's own help center on November 15, 2026. That marks the moment the company went on the record about a security incident affecting the service.doorayhelp.oc.nhncloud.comdoorayhelp.oc.nhncloud.com · rssOpen original sourceSee in source list
The account of how it unfolded comes from DailyDarkWeb's reading of that notice. Attackers allegedly guessed password-reset codes, the one-time passcodes that prove a reset request is legitimate, and separately exploited API keys that were already exposed. That combination opened the door to work files and account data. The remedy, pulling all service and Admin keys at once, cut off the intruders but also disrupted every integration relying on those keys.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
The reported breach touches two sensitive layers at once: the documents teams store inside a work tool, and the account data that decides who can enter. Revoking all API keys rather than a subset suggests the company could not cleanly separate legitimate from malicious use. Customers therefore face a double problem, a possible data exposure plus broken automations, the scheduled scripts and app links that quietly move work between systems.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
The guidance shared alongside the notice is practical. Reset your Dooray password. Turn on two-factor authentication, which asks for a second proof of identity beyond the password. And review your connected workflows, both to spot anything suspicious and to rebuild the ones that stopped working when the keys were revoked.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
Two things are on the record so far. Dooray's help center now carries an official security notice, and a widely shared post by DailyDarkWeb summarizes what it says, including the reset-code guessing, the exposed keys, the confirmed leak, and the full revocation.doorayhelp.oc.nhncloud.comdoorayhelp.oc.nhncloud.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Everything else is open. The summary does not say how many accounts were affected, which data fields were taken, how the reset codes became guessable, or who the attackers were. Because the notice's full text was not retrieved in this evidence batch, every specific claim currently rests on a single secondary account.doorayhelp.oc.nhncloud.comdoorayhelp.oc.nhncloud.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
Public discussion is thin so far. The visible conversation amounts to DailyDarkWeb's post on X, which shared a screenshot of the notice and linked to the official page. In the available evidence there are no victim accounts, no attacker claims of credit, and no statements from NHN beyond the notice itself.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The public record starts and nearly ends at the same moment. Both the official notice and the first discussion post carry a timestamp of November 15, 2026, so the company's statement and the first wave of public awareness arrived together. Nothing in this batch shows earlier signals, such as leaked samples or attacker chatter, predating the disclosure.doorayhelp.oc.nhncloud.comdoorayhelp.oc.nhncloud.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 0 engagements.
Technical detail
The summary points to two distinct failure modes. Reset-code guessing means the one-time codes that validate a password reset were predictable or unprotected against repeated attempts, in effect letting an attacker take over an account without ever knowing the original password. Exposed API keys are the second path: these long credential strings authenticate programs directly, bypassing passwords entirely.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The remediation choice is also telling. Revoking all service and Admin keys severs attacker access immediately, but it cannot distinguish friend from foe, so every legitimate automation, webhook, and connected app built on those keys goes dark with it. Recovery likely means customers reissuing and reconnecting credentials one by one.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
This story rests on two items. The first is the official Dooray help center notice, the primary source, dated November 15, 2026, though its full text was not retrieved here. The second is DailyDarkWeb's post on X, which summarizes the notice and attaches a screenshot. Treat the specifics as reported rather than independently confirmed until the notice text or a direct NHN statement is captured.doorayhelp.oc.nhncloud.comdoorayhelp.oc.nhncloud.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x
- doorayhelp.oc.nhncloud.comdoorayhelp.oc.nhncloud.com · rss


