In 30 seconds
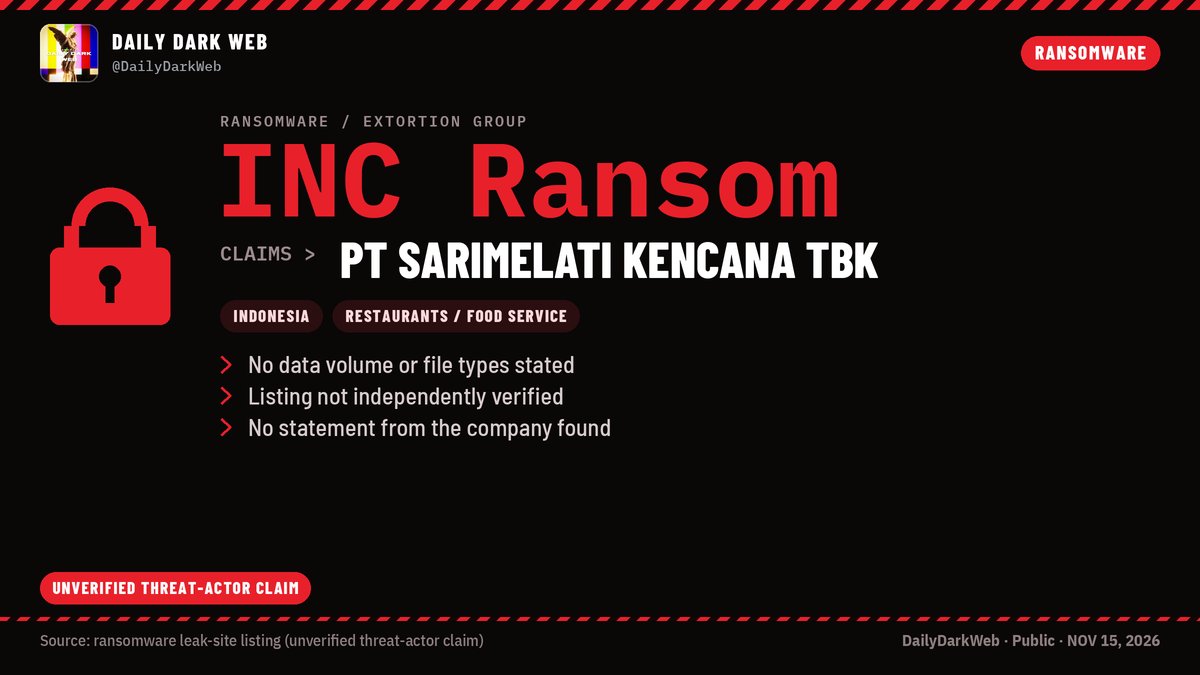
Ransom group INC Ransom has added PT Sarimelati Kencana Tbk, the company that runs Pizza Hut restaurants in Indonesia, to its leak site, according to a November 15 post from dark web monitoring account DailyDarkWeb. The post identifies the target as an Indonesia Stock Exchange listed franchisee of YUM! Brands and a subsidiary of PT Sriboga Raturaya. The listing itself states no data volume, no file types, and no deadline.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The listing amounts to a claim by INC Ransom that it attacked the operator, and that claim is unverified. No statement from Sarimelati Kencana has been found, and the monitoring account itself tells readers to treat it as an unverified threat actor claim, not confirmation of a breach.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
The story went public on November 15, 2026, when DailyDarkWeb reported a new entry on INC Ransom's leak site, the extortion channel where ransom groups name victims and pressure them with the threat of publishing data. A screenshot of the listing accompanies the post, and that screenshot is essentially the entire public evidence base so far.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The named target, PT Sarimelati Kencana Tbk, trades on the Indonesia Stock Exchange and operates the Pizza Hut restaurant chain in Indonesia as a franchisee of YUM! Brands. It sits under parent company PT Sriboga Raturaya.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The listing is unusually bare. It does not say how much data was taken, what kind of files are involved, or when any deadline expires, which leaves the attackers' word as the only basis for assuming a breach happened at all.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
INC Ransom is a long-running data theft and extortion operation, and DailyDarkWeb notes it has repeatedly hit Indonesian companies in 2026, including food and beverage firms. That track record makes the claim worth watching, though it proves nothing about this particular target.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
A national restaurant chain operator is a rich target if the claim holds up. The analyst note flags potential exposure of employee records, supplier and franchise contracts, and possibly delivery customer data, exactly the kind of information that feeds phishing and fraud long after any headline fades.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
Watch official channels first. A statement from Sarimelati Kencana, a disclosure through the Indonesia Stock Exchange, or word from franchisor YUM! Brands would be the first credible signal either way, and none has appeared yet.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
In the meantime, the practical warning is about scams. Customers and staff should be wary of phishing emails, texts, or fake promotions that use Pizza Hut Indonesia branding, since a claimed breach is a ready-made hook for exactly that kind of fraud.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
What is established is narrow. One monitoring account reports a leak site listing naming Sarimelati Kencana, that listing states no data volume, file types, or deadline, and the company has issued no statement. Nothing in the public record confirms a breach.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What is unknown is everything that matters: whether any data was actually taken, whose data it might be, whether ransom talks are happening behind the scenes, and whether a deadline or sample dump will follow. Until the company or an independent party confirms something, this stays a threat actor's assertion.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
Two parties have spoken so far. INC Ransom speaks only through its leak site listing, which names the company and says nothing else. DailyDarkWeb, which surfaced the listing, is explicit about its weight: treat it as an unverified threat actor claim, not confirmation of a breach.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The company itself has been silent. No statement from Sarimelati Kencana has been found, which leaves the attackers' version of events standing unchallenged in public for now.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The timeline is short. On November 15, 2026, DailyDarkWeb reported the listing, and there has been no visible movement since: no deadline set on the leak site, no data samples released, no company response, and no independent verification.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
How this develops from here follows familiar patterns. Either the group posts a deadline or data samples, the company confirms or denies an incident, or the listing quietly disappears if a payment or negotiation resolves it. None of those steps has happened yet, and the story still rests on a single researcher's report.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 1 engagements.
Technical detail
The mechanism is leak site extortion, meaning the group names a victim on its site and leans on the threat of publishing stolen data. This listing skips the specifics that usually give such entries teeth: it states no data volume, no file types, and no countdown deadline.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
DailyDarkWeb characterizes INC Ransom as a long-running data theft and extortion operation with repeated Indonesian victims in 2026, including food and beverage companies. That suggests a crew familiar with the sector rather than one testing a random target. What it does not show is whether anything was actually taken here.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
The evidence base is one item: a November 15, 2026 post on X by DailyDarkWeb, a dark web monitoring account, including a screenshot of the INC Ransom leak site listing. No company statement, exchange filing, or independent confirmation appears in the available material.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Every detail in this story so far, from the listing's existence to the corporate background, traces back to that single post. A second source or an official statement would change the picture, and until then the appropriate posture is caution, not alarm.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x


