[Single source] Fortinet patches critical unauthenticated FortiMail flaw
Fortinet patched CVE-2026-126147, a FortiMail API path traversal that may allow unauthenticated code execution, according to DailyDarkWeb. The source says there is no known exploitation. Upgrade to 8.0.2, 7.6.7, or 7.4.9 or later; 7.2 deployments must migrate.
In 30 seconds
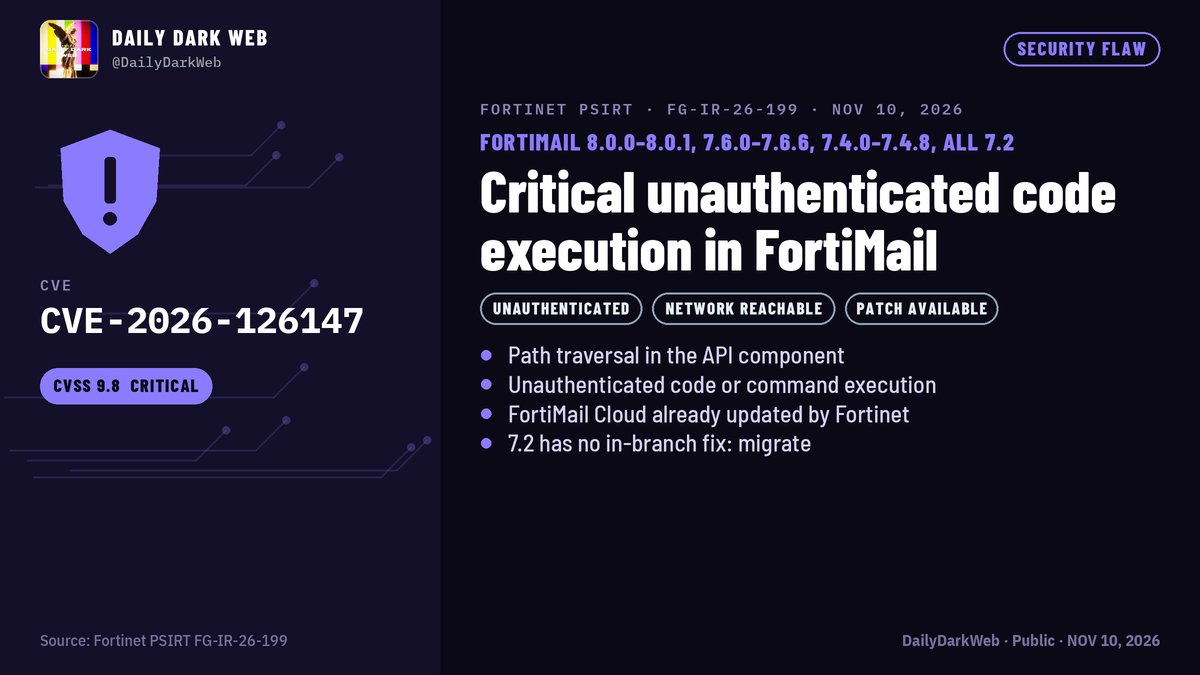
The latest detailed item says Fortinet patched CVE-2026-126147, a critical FortiMail API path traversal that may let an unauthenticated attacker run code. It lists fixed releases and says FortiMail Cloud is already protected, but the supplied Fortinet advisory has no body text to independently verify those details.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listfortiguard.fortinet.comfortiguard.fortinet.com · rssOpen original sourceSee in source list
What happened
DailyDarkWeb reports that Fortinet addressed CVE-2026-126147 on November 10 and assigns it a CVSS score of 9.8. The post describes the vulnerability as path traversal in a FortiMail API, meaning crafted input could reach an unintended file-system path, potentially leading to code execution without authentication.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
If the reported behavior is accurate, the combination of remote access, no authentication requirement and possible code execution makes the flaw especially serious for internet-reachable mail infrastructure. The evidence does not establish the exact attack conditions or resulting privileges.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
The reported remediation is to upgrade to FortiMail 8.0.2, 7.6.7 or 7.4.9 and later. Deployments on the 7.2 branch are said to require migration rather than an in-branch update. Administrators should confirm the applicable path against Fortinet advisory FG-IR-26-199 before changing production systems.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listfortiguard.fortinet.comfortiguard.fortinet.com · rssOpen original sourceSee in source list
Confirmed and still uncertain
The batch identifies the vulnerability, the reported severity and the claimed fixed releases. DailyDarkWeb says exploitation is not known, but the supplied evidence includes no telemetry, incident analysis or advisory text that independently demonstrates whether attacks have occurred.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listfortiguard.fortinet.comfortiguard.fortinet.com · rssOpen original sourceSee in source list
What people are saying
DailyDarkWeb characterizes CVE-2026-126147 as a critical, unauthenticated code-execution risk and urges upgrades or migration. No direct statement from a Fortinet representative is included in the batch.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listfortiguard.fortinet.comfortiguard.fortinet.com · rssOpen original sourceSee in source list
Evolution
The available account dates the issue to November 10, then reports that Fortinet released fixes for supported branches and had already remediated FortiMail Cloud. The evidence does not provide an earlier discovery timeline, disclosure history or patch sequence.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 1 engagements.
Technical detail
The post calls the bug an API path traversal that may enable unauthenticated code execution. It supplies no vulnerable endpoint, proof of concept, request format, privilege level or explanation of how traversal becomes code execution, so the exploitation chain remains unspecified here.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
The batch contains a primary Fortinet PSIRT URL for FG-IR-26-199, but no title or advisory body, plus one DailyDarkWeb post carrying all substantive vulnerability, version and exploitation-status claims. Those claims should therefore be treated as attributed reporting rather than independently confirmed details from the supplied primary record.fortiguard.fortinet.comfortiguard.fortinet.com · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x
- fortiguard.fortinet.comfortiguard.fortinet.com · rss