In 30 seconds
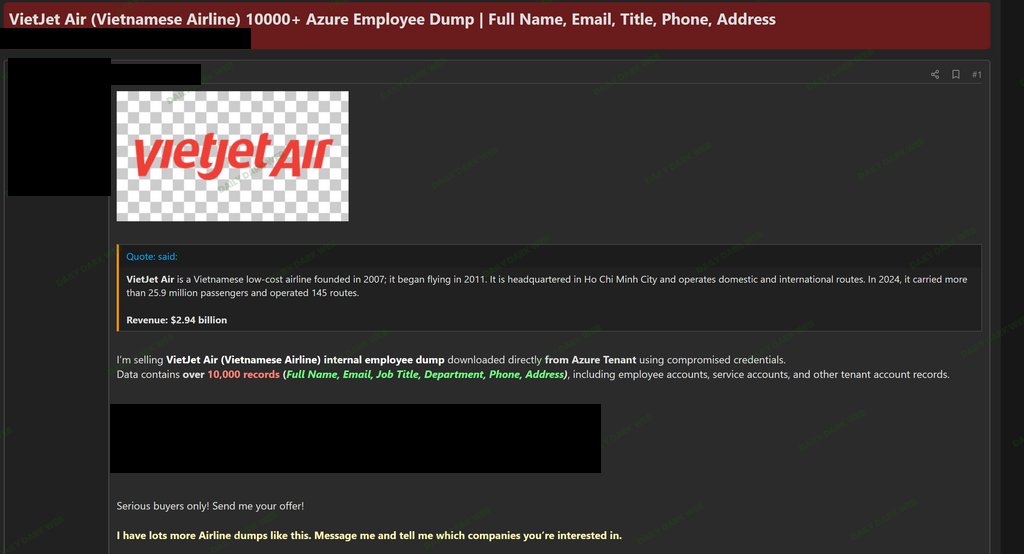
A dark web monitoring account, DailyDarkWeb, went public today, November 16, with a claim worth a raised eyebrow: someone says they got into VietJet Air's cloud and is now selling the airline's internal staff directory. The post carries a screenshot of the alleged listing and an explicit caution that nothing is verified yet.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
Here is the chain as the evidence lays it out. On November 16, 2026, DailyDarkWeb posted on X that a threat actor is offering the directory for sale. The post relays the seller's claims and attaches an image of the listing.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
According to those claims, the actor used compromised credentials to reach VietJet's Microsoft Azure environment, essentially the airline's back office in the cloud, extracted the internal directory from there, and put it up for sale. Every link in that chain is the seller's own account of events.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
Why care about what sounds like a phone list? Because, as the analyst note attached to the post points out, a staff directory is a ready-made target list. Names, titles and departments let a criminal craft convincing phishing emails, and payroll or vendor fraud works far better when the attacker knows exactly who handles payments.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
There is a human layer too. If the data is real, thousands of employees would be exposed to scams that arrive looking internal and legitimate, at work and possibly at home. That is the risk scenario the claim opens up, not a confirmed outcome.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
Until VietJet confirms or denies the claim, the sensible posture is caution. Employees should treat unexpected messages about payroll, benefits or vendor payments with extra suspicion and verify any request through a channel they already trust before acting on it.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
On the corporate side, the claimed entry point, compromised credentials, points to the standard playbook: reset exposed accounts and review Azure sign-in activity for anything odd. This is precaution built on a claim, not an admission that a breach happened.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
What is established is narrow: a public post reports that a sale listing exists, the listing makes specific claims about scope and source, and VietJet has not commented, at least nowhere in the evidence available here.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What is missing is everything that matters. Whether the data is real, whether credentials were actually compromised, who the seller is, how current the records are, and whether anyone has bought the directory. No samples and no technical proof appear in the public evidence.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
DailyDarkWeb, the account that surfaced the story, is upfront about the limits. It tags the whole thing as an unverified threat-actor claim and flags the airline's silence rather than presenting it as a confirmed breach.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The seller, whose identity the evidence does not show, tells a clean story of 10,000-plus records taken straight from the company's Azure tenant. That is the actor's version, and at this stage it is the only version on the table.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The public trail is short. The story surfaced on November 16 through the DailyDarkWeb post, and within the evidence available there is no earlier chatter, no follow-up reporting and no company response to extend or correct the picture.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What would move the needle from here: a sample of the data, independent confirmation from researchers, or a statement from VietJet. Until one of those arrives, the claim stands entirely alone.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 0 engagements.
Technical detail
What the public evidence does not show: record samples, dates for the alleged access, proof the credentials worked, or the forum where the sale is running. The screenshot in the post is the full extent of the visible technical material.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
This item rests on a single source: an X post by DailyDarkWeb published on November 16, 2026, which relays the seller's claims and includes a screenshot of the alleged listing credited to the account.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
That is thin ground. One secondhand report of an anonymous seller, no corroboration from VietJet, researchers or other monitors in this batch, and no independent look at the data. Everything about the breach itself stays in the alleged column until that changes.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x


