In 30 seconds
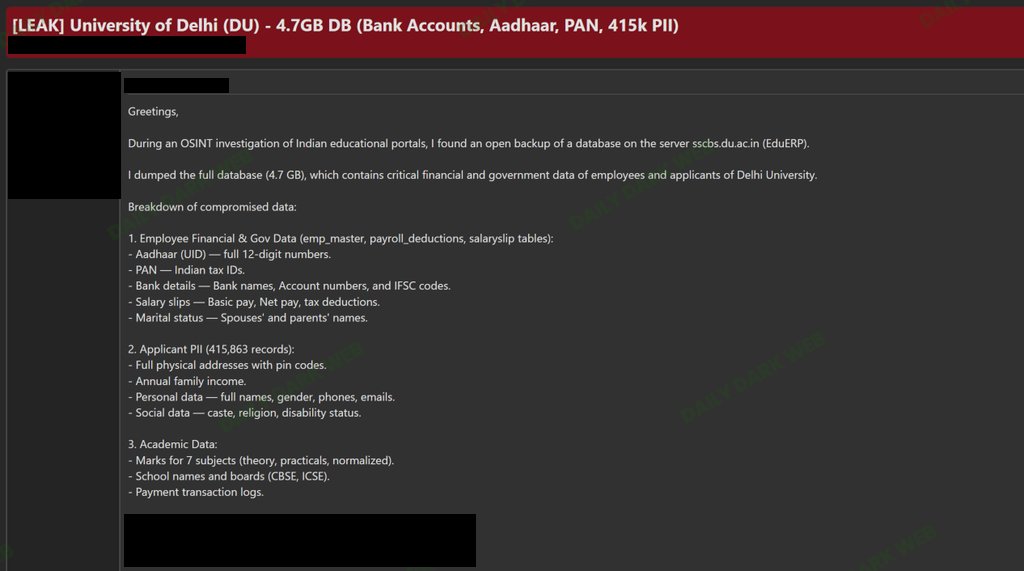
Here is where things stand: on November 17, 2026, the dark web monitoring account DailyDarkWeb reported that a threat actor claims to have dumped a 4.7GB database from the University of Delhi, saying the data was found as an open backup on a college server running EduERP, software used to run university administration.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The claimed contents read like a worst case for identity theft: staff Aadhaar numbers (India's national ID), PAN tax IDs, bank account details and salary slips, plus personal records on 415,863 applicants, including addresses, family income, phone numbers, emails, caste, religion and disability status. None of this is confirmed, and the university has not commented.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
According to the threat actor's account as relayed by DailyDarkWeb, there was no hacking in the classic sense. The actor says they found a backup file sitting open on a University of Delhi college server running EduERP, in effect a saved copy of the database that anyone who found it could download, and pulled 4.7GB from it.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The actor claims the dump blends two very different groups. One is university staff, whose national ID numbers, tax IDs, bank details and salary slips would be exposed. The other is 415,863 applicants, whose files allegedly include addresses, family income, contact details, and caste, religion and disability status.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
The mix is what makes this claim alarming, as DailyDarkWeb's own analyst note points out: Aadhaar, PAN and bank details together are enough for serious identity and financial fraud, from account takeovers to credit taken out in someone else's name.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The applicant data adds a second layer of potential harm. Caste, religion, disability status and family income are details that can be weaponized for discrimination, harassment or precisely targeted scams, and the people affected, mostly applicants rather than staff, may have no idea their files sat on such a system.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
With the breach still unconfirmed, the practical move is defensive. Staff whose Aadhaar, PAN or bank details could be in the dump should watch bank statements and account activity closely, since those three pieces are exactly what fraudsters need.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Applicants should treat any call, message or email that quotes their personal details as a red flag, especially requests for payments or codes to fix a records problem. A statement from the University of Delhi would clarify who is actually affected, and none has come yet.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
What is on the record so far is narrow: a single X post by DailyDarkWeb, dated November 17, 2026, describing a threat actor's claim, with the account itself flagging the claim as unverified and noting that the university has not commented.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What is unknown is everything that would make this a confirmed incident: whether the dump exists, whether it genuinely comes from a University of Delhi system, how many staff records it holds, whether anyone else downloaded the open backup, and whether the data has been sold or shared further.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
The only public voice in the evidence so far is DailyDarkWeb itself, a monitoring account that specializes in flagging dark web activity. Notably, it leads with caution rather than certainty, calling the leak alleged and attaching an analyst note that labels the claim unverified.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The threat actor's original post does not appear in this batch, and the University of Delhi has said nothing publicly, so every specific detail currently reaches the public secondhand.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The timeline is short: the claim surfaced on November 17, 2026, in DailyDarkWeb's post, and no earlier report, data sample or corroboration appears in the available evidence. This is day one of the story, not the latest chapter of a long-running one.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
How it evolves from here depends on moves that have not happened yet: a denial or confirmation from the university, independently checked proof of a data sample, or the actor publishing the dump. Any one of those would shift the picture from rumor to incident.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 4 engagements.
Technical detail
The technical claim centers on EduERP, a university administration system that handles records and payroll, and on what the actor describes as an open backup: a saved copy of the database left accessible on a server, so that finding it is enough to download it, with no password break-in required.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
If that description is accurate, the failure mode would be a misconfigured server rather than malware, which matters for how universities audit these systems. Nothing in the current evidence verifies that the server or the backup ever existed as described.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
This item rests on one source: the November 17, 2026 post by DailyDarkWeb on X, which packages the threat actor's claim, a claimed contents list, and the account's own analyst note stating the claim is unverified and that DU has not commented.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The credibility ceiling is therefore low until more arrives. A statement from the University of Delhi, the actor's original listing, or an independently verified sample of the data would each change the assessment. For now, every sentence above traces back to that single report.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x


