In 30 seconds
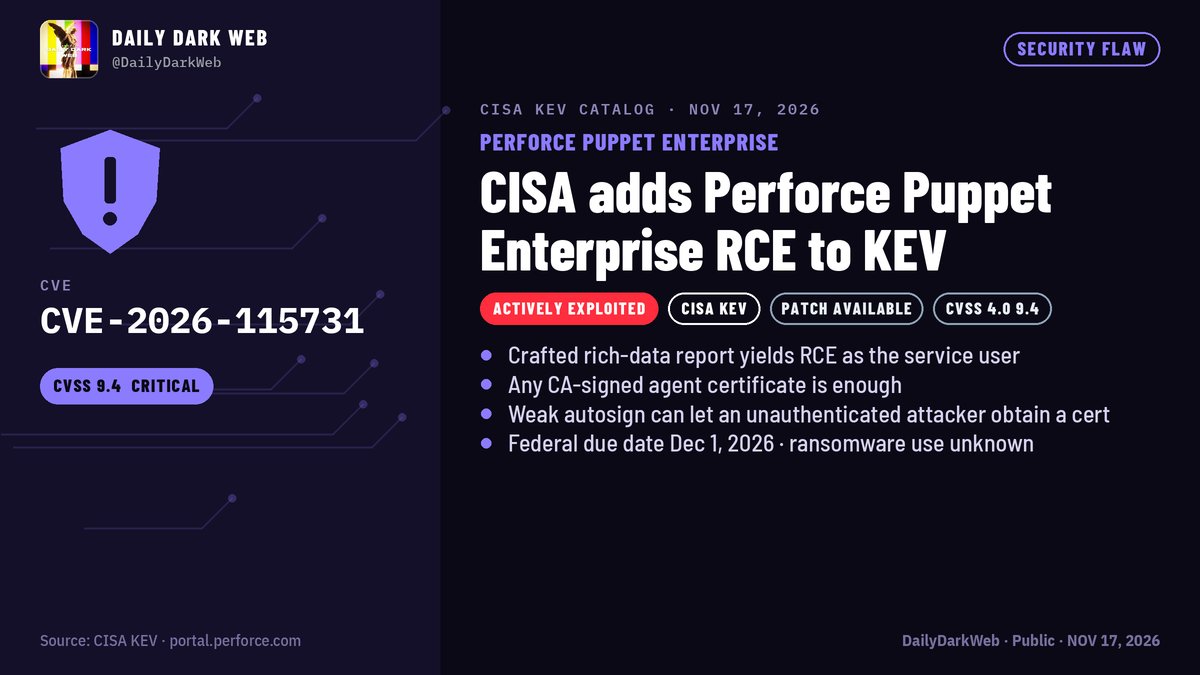
CISA has added CVE-2026-115731 to its Known Exploited Vulnerabilities catalog, the KEV list where the US cyber agency records bugs it says are under active attack. The target is Puppet Enterprise, Perforce's platform for managing configuration across fleets of servers. The flaw sits in the code that processes agent reports, and it lets any client holding a CA-signed agent certificate, in plain terms a valid identity issued by the deployment's own certificate authority, run arbitrary code on the Puppet Server as the service user.CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
There is a sharper edge. If the certificate authority automatically signs certificate requests without strong verification, an unauthenticated attacker on the network can obtain a valid certificate and exploit the flaw with no credentials at all. CISA requires vendor mitigations, sets a December 1, 2026 deadline for federal agencies, and records known ransomware use as unknown.CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
What happened
The paper trail starts with the vendor. Perforce hosts a dedicated advisory on its support portal under the title report deserialization code execution, the official home for this vulnerability's documentation.portal.perforce.comportal.perforce.com · rssOpen original sourceSee in source list
On November 17, 2026, CISA added the CVE to the KEV catalog. The entry orders mitigations per vendor instructions, compliance with BOD 26-04, the binding directive that prioritizes security updates by risk, and adherence to CISA's forensics triage requirements. For cloud services the stated fallback is to follow the directive or discontinue the product if mitigations are unavailable. The clock for federal agencies stops on December 1, 2026.CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
DailyDarkWeb, an X account tracking underground activity, supplies the backstory. It says its November 5 post had already flagged public exploit details, but neither related CVE was in KEV at the time. As of this update, CVE-2026-115731 is in and companion identifier CVE-2026-115732 is not.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
Puppet is the machine that decides what every managed server should look like, software, settings, the lot. Code execution on the Puppet Server is therefore not just one compromised host. It is a potential lever over the configuration pushed to the whole fleet, which is why a report-processing bug deserves urgent attention.CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
The listing also has teeth. CISA tells stakeholders to evaluate each asset's internet exposure, federal agencies must remediate by December 1, 2026, and the entry explicitly leaves discontinuing the product on the table when mitigations are unavailable for cloud use.CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
What to do
Apply mitigations in accordance with vendor instructions, and fold in CISA's forensics triage requirements so any prior compromise can actually be investigated. Take a hard look at whether your Puppet Server is reachable from the internet.CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
On versions, the numbers circulating come from DailyDarkWeb's summary of the vendor advisory: fixed releases are Puppet Enterprise 2023.8.13, 2025.12.1 and 2026.0.1, and puppetserver needs a restart after updating. Perforce's advisory page is the authoritative reference for the exact steps.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listportal.perforce.comportal.perforce.com · rssOpen original sourceSee in source list
Then audit one setting above all: certificate authority behavior. CISA's entry warns that a CA which auto-signs requests without strong verification hands unauthenticated attackers a valid certificate, which is the ingredient that removes authentication from this attack.CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
Confirmed and still uncertain
On solid ground: the flaw is real, it lives in Puppet's report-processing code, any CA-signed agent certificate is enough to exploit it, and CISA now treats it as actively exploited. The entry names no victims, no actors and no campaign details, and it marks known ransomware use as unknown.CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
Still foggy: who is exploiting it and since when. DailyDarkWeb reports that public exploit details existed by November 5, before the KEV listing. The account also notes CVE-2026-115732 remains outside the catalog, leaving that companion flaw's status open.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
The loudest public voice in this batch is DailyDarkWeb. Its message is blunt: patch Puppet Enterprise now, and review whether your certificate authority auto-signs requests. The account frames the KEV addition as the moment its earlier reporting on public exploit details turned into government-confirmed exploitation.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The flaw did not appear this week. Fixes were already shipped and exploit details were already public in early November, per DailyDarkWeb's coverage. What changed now is the evidence bar: a KEV entry signals CISA's own determination that exploitation is happening, which turns a patch-eventually item into a patch-today one for anyone running Puppet Enterprise.CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
3 independent groups, 2 updates, and 0 engagements.
Technical detail
Mechanically this is a deserialization flaw, meaning the server unpacks incoming data structures without validating them enough. A client sends a report through a PUT request containing a crafted rich-data type, a deliberately shaped object, and the act of unpacking it yields arbitrary code execution on the Puppet Server as the service user.CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
The authentication picture makes it worse. Any certificate signed by the deployment's certificate authority qualifies, and every legitimate Puppet agent already holds one. Where the CA auto-signs requests without strong verification, an unauthenticated network attacker can mint a certificate at will, which is the scenario CISA explicitly calls out.CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
Sources and evidence
Primary grounding: the CISA KEV entry for CVE-2026-115731, source of the deadline, the required actions and the technical description, plus Perforce's advisory page on its support portal. The advisory arrived in this batch without body text, so it is referenced as the vendor's authoritative document rather than quoted.CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source listportal.perforce.comportal.perforce.com · rssOpen original sourceSee in source list
Supporting material: the CISA KEV catalog feed and one discussion post from DailyDarkWeb, which supplies the fixed version numbers, the restart step and the November 5 backstory. Those specifics are third-party claims until read directly against the vendor advisory, and the batch contains no victim media or independent forensic reports.CISA Known Exploited Vulnerabilities Catalogcisa.gov · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- CVE-2026-115731: Perforce Puppet Enterprise (Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability)nvd.nist.gov · kev
- DailyDarkWebx.com · DailyDarkWeb · x
- portal.perforce.comportal.perforce.com · rss
- CISA Known Exploited Vulnerabilities Catalogcisa.gov · rss