In 30 seconds
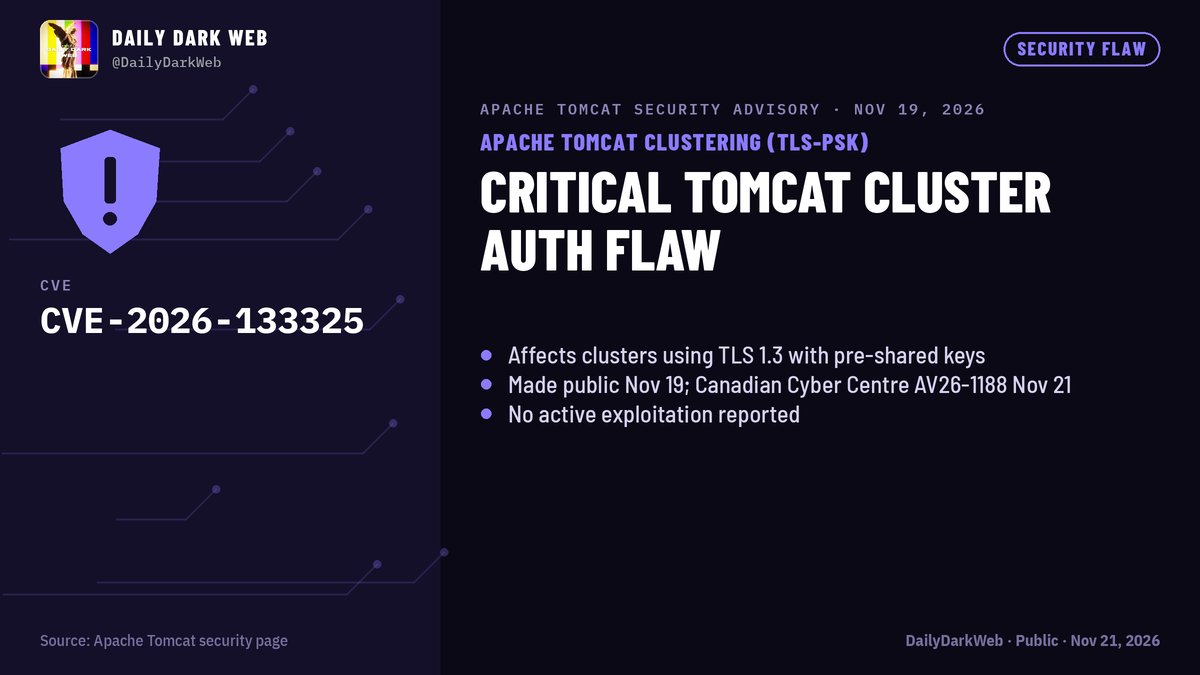
The latest supplied report says fixed Tomcat releases for CVE-2026-133325 have not yet shipped. It attributes to Apache an interim recommendation for affected clusters: use TLS 1.2 with pre-shared keys instead of TLS 1.3 until a fix becomes available.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
The report says the flaw could allow an unauthenticated node to join a Tomcat cluster when TLS 1.3 and pre-shared keys are used together. The supplied evidence does not independently demonstrate exploitation or identify an affected organization.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
If the reported behavior is accurate, the weakness affects the cluster admission boundary: a node that has not been authenticated could reportedly become part of the cluster. The evidence does not specify what access or follow-on actions such membership would provide.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
Administrators using the described combination should review their cluster configuration. The only mitigation stated in the supplied report is to use TLS 1.2 with pre-shared keys until fixed releases ship.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
The batch identifies CVE-2026-133325, the TLS 1.3 cluster condition and the reported absence of fixed releases. It does not provide affected version ranges, technical prerequisites beyond pre-shared keys, evidence of active exploitation, patch dates or the consequences of a rogue node joining.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listtomcat.apache.orgtomcat.apache.org · rssOpen original sourceSee in source list
What people are saying
DailyDarkWeb characterized the issue as critical and said Apache had issued the warning and interim TLS 1.2 recommendation. Because the Apache security item in this batch contains no body text, those substantive details remain an attribution from the discussion post rather than independently reproduced primary-source statements here.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listtomcat.apache.orgtomcat.apache.org · rssOpen original sourceSee in source list
Evolution
The evidence captures the issue at a pre-fix stage: a vulnerability is being reported, an interim configuration change is recommended and corrected releases are still pending. No earlier disclosure timeline or later remediation update appears in the supplied batch.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 0 engagements.
Technical detail
The described failure mode concerns authentication during cluster joining under TLS 1.3 with pre-shared keys. Beyond the claim that an unauthenticated node could join, the batch provides no protocol trace, proof of concept, vulnerable code path or severity score.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
The supplied evidence consists of an Apache Tomcat 11 security-page item without captured body text and a DailyDarkWeb post linking the warning to that page. The post supplies the vulnerability number, affected configuration, claimed behavior, patch status and mitigation, but the batch does not include the underlying Apache advisory text needed to verify those details directly.tomcat.apache.orgtomcat.apache.org · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x
- tomcat.apache.orgtomcat.apache.org · rss