In 30 seconds
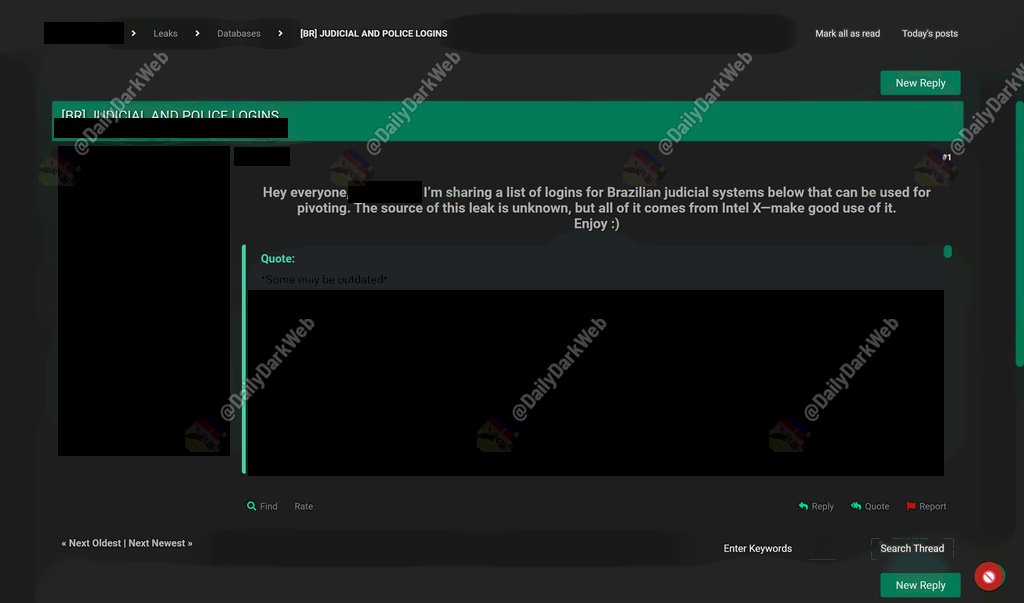
A threat actor on an underground forum is circulating what they claim are login credentials for Brazilian judicial and police systems, pitching them as useful for "pivoting", which means using one foothold to push deeper into a network. The visible sample shows login page URLs for state civil police and other government portals, numeric usernames, passwords in plain readable text, and browser labels typical of infostealer logs, the records produced by malware that harvests saved passwords from infected devices.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Treat the headline with care. The actor admits the source of the data is unknown and that some entries may be outdated, and the report itself is marked unverified.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
The item surfaced through DailyDarkWeb, an account that tracks underground activity, which reported that a threat actor was sharing a list presented as credentials for Brazilian judicial and police systems. According to the report, the actor framed the material as a starting point for pivoting into government systems.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What is actually visible is narrower than a database dump. The sample shows login page URLs on state civil police and other government portals, usernames in the form of numeric IDs, passwords in plaintext, and browser source labels of the kind found in infostealer logs.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
The analyst note attached to the report offers a calmer read: the format looks like credentials collected from infostealer infected devices and repackaged from earlier dumps, not the result of a breach of the judicial or police systems themselves.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
That distinction matters, but it does not erase the risk. Working accounts on police training or judicial portals, if any of the entries still function, could give attackers a foothold for phishing, data theft or deeper access.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
No official guidance exists yet, so the sensible response follows from the exposure itself. Agencies whose portals appear in the sample would want to identify the exposed accounts, reset those passwords, and review recent login activity for anything unusual.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The affected agencies have not commented, and the report carries an explicit unverified label, so any action taken now is precautionary rather than a response to a confirmed breach.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
Established at the level of reporting: a forum post exists, an actor is promoting a claimed credential list, and the visible sample matches the shape of infostealer data, with numeric usernames, plaintext passwords and browser labels.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Still open: whether any login actually works, where the list came from, since the actor admits the source is unknown, and how current the entries are, with the actor conceding that some may be outdated. No affected agency has commented.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
The actor's own caveats do the skeptic's work here. In the listing, they admit the source of the data is unknown and that some entries may be outdated.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
DailyDarkWeb, which surfaced the item, keeps its footing careful: the post is labeled unverified, the read is that this is repackaged infostealer material rather than a breach of the systems themselves, and the note flags that affected agencies have not commented.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The framing has already been narrowed once. The headline version was judicial and police system logins shared by a threat actor. The analyst note that came with the report pulled that back toward credential repackaging, pointing to infostealer collection rather than a compromise of the systems themselves.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Since that note, nothing has moved the picture. There is no agency comment, no independent confirmation and no reported test of the credentials in this batch.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 0 engagements.
Technical detail
Three markers stand out in the sample. Usernames are numeric IDs rather than email addresses. Passwords appear in plaintext, readable exactly as typed. Each entry carries a browser source label, the fingerprint associated with infostealer logs when saved credentials are exported from an infected machine.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
On those markers, the analyst note leans toward a specific origin: credentials harvested from infostealer infected devices and repackaged from earlier dumps, with the actor unable or unwilling to say where the list came from.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
This item rests on one secondary source: a post by DailyDarkWeb on X that includes a screenshot of the forum listing. The post itself carries an unverified label and states that the affected agencies have not commented.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Independent confirmation would take the shape of agency statements, password resets or login anomalies on the named portals, or a second researcher matching the entries to known infostealer dumps. None of that appears in this batch.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x


