In 30 seconds
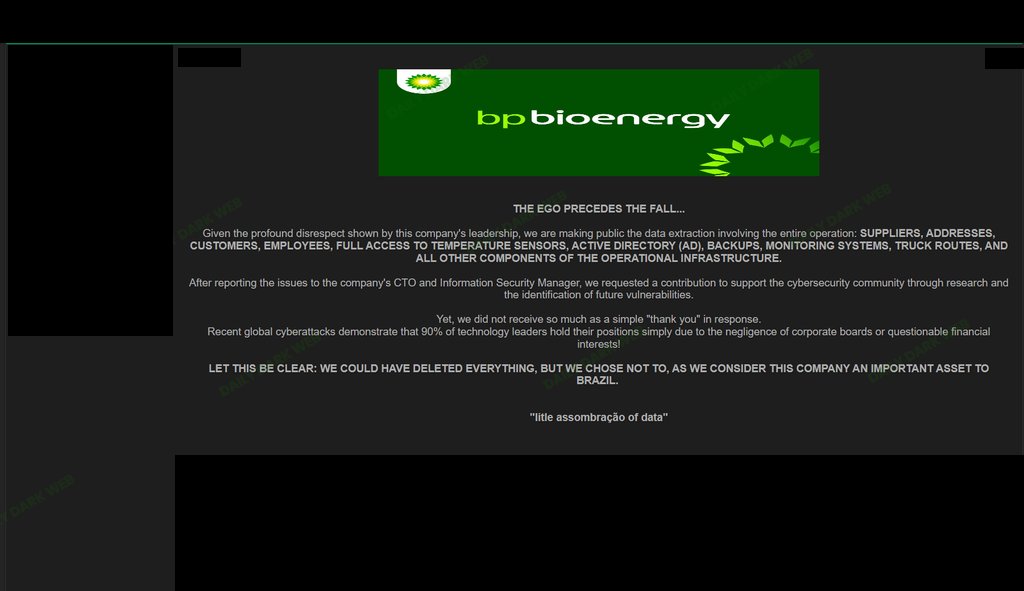
DailyDarkWeb reports that a threat actor claims to have breached BP Bioenergy and begun publishing a 4.5GB data extract. The report explicitly labels the claim unverified and says there was no official statement at the time of publication.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
According to DailyDarkWeb, the actor alleges it found security flaws, reported them to company security leaders and released data after payment was refused. This account comes through a secondary report and does not establish that access, contact or publication actually occurred.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
If the claims are genuine, the incident could combine privacy exposure with operational risk: the actor allegedly accessed personal and business records, identity infrastructure, backups, monitoring systems, temperature sensors and transport information. The evidence supplied does not demonstrate disruption or manipulation of those systems.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
BP Bioenergy should urgently test the allegation against its own logs and systems, particularly Active Directory, backups, monitoring tools, sensors and accounts connected to supplier, customer and employee records. Because the claim remains unverified, the immediate priority is determining whether access occurred, preserving evidence and containing any confirmed exposure.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
What is known from the supplied evidence is that DailyDarkWeb published the allegation and described it as unverified. It remains unknown whether BP Bioenergy was breached, whether 4.5GB was actually obtained or released, what records may be authentic, how long any access lasted and whether operational technology was affected.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
DailyDarkWeb characterizes the reported sequence as a classic extortion pattern and warns that alleged access to operational technology and sensors could create operational risk if real. That is the publisher's assessment, not confirmation of the actor's account.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The reported chain begins with alleged discovery of flaws and access to company systems, followed by an alleged approach to security leaders, refusal of payment and publication of a purported 4.5GB extract. No independent confirmation or subsequent company response appears in the supplied evidence.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 0 engagements.
Technical detail
The most consequential technical allegation is access to Active Directory, the system commonly used to manage organizational identities and permissions, alongside backups and operational monitoring. The post provides no indicators of compromise, exploit details, sample validation or forensic evidence with which to verify those claims.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
The evidence supplied consists of one DailyDarkWeb post on X with an attached image. It relays a threat actor's claims while expressly calling them unverified and noting the absence of an official statement, so the alleged breach and data leak cannot be treated as established facts.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x


