In 30 seconds

CISA has added CVE-2026-114713, a high-severity UnrealIRCd command-injection flaw, to its Known Exploited Vulnerabilities catalog. Federal agencies must apply the prescribed mitigations by November 16, 2026, or discontinue the product if mitigations are unavailable.CVE-2026-114713: UnrealIRCd UnrealIRCd (UnrealIRCd Improper Neutralization of Delimiters Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source listAttackers Exploit UnrealIRCd Flaw That Enables Server-Level Command Injectionthehackernews.com · rssOpen original sourceSee in source list
What happened
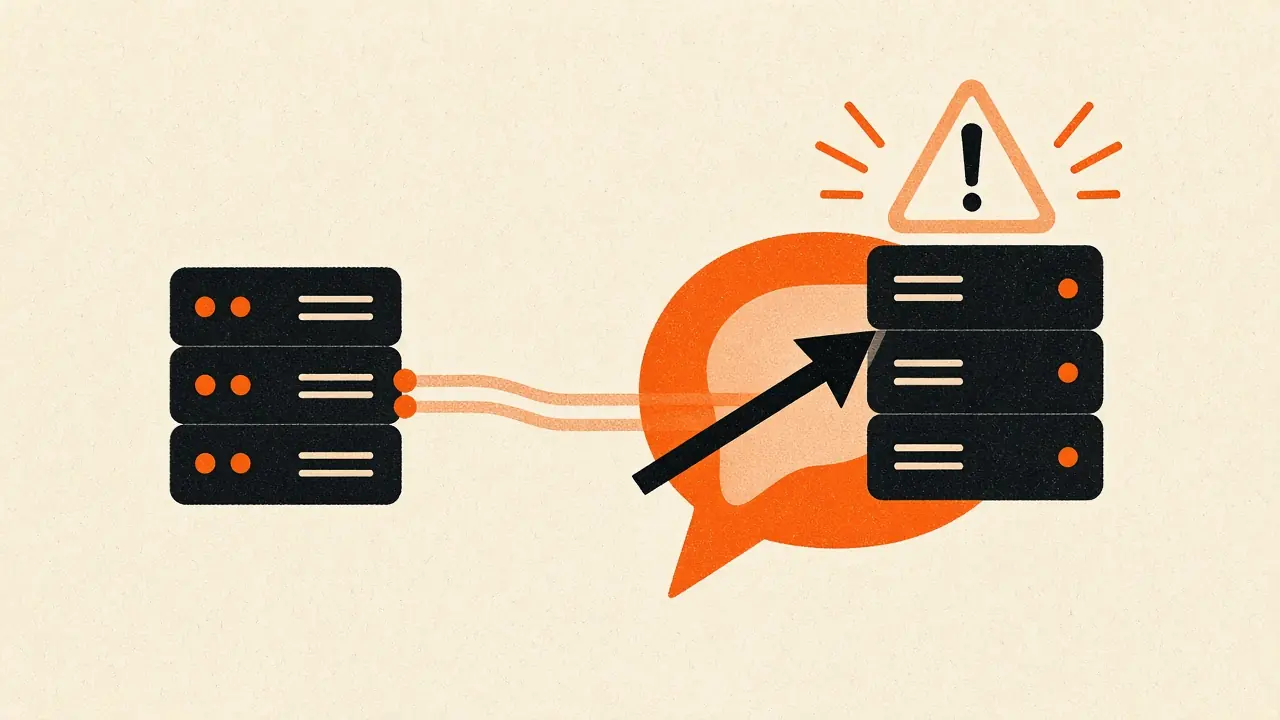
The flaw allows any user on an IRC network containing two or more linked UnrealIRCd servers to inject server-to-server commands. Those commands are then executed with the authority of a server rather than the limited permissions of the user.CVE-2026-114713: UnrealIRCd UnrealIRCd (UnrealIRCd Improper Neutralization of Delimiters Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
Why it matters
Because injected commands receive server authority, exploitation could give an ordinary network user capabilities beyond their normal account. The documented prerequisite narrows the exposure to networks with at least two linked servers, but makes affected linked deployments a priority for review.CVE-2026-114713: UnrealIRCd UnrealIRCd (UnrealIRCd Improper Neutralization of Delimiters Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
What to do
Administrators should identify internet-exposed UnrealIRCd assets, check whether they participate in a network of linked servers, and apply the vendor's mitigations. CISA directs covered federal organizations to follow BOD 26-04 and its forensic triage requirements, with discontinuation advised when no mitigation is available.CVE-2026-114713: UnrealIRCd UnrealIRCd (UnrealIRCd Improper Neutralization of Delimiters Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
Confirmed and still uncertain
The vulnerable condition and federal remediation deadline are documented. The supplied evidence does not identify affected versions, exploitation methods, victims, indicators of compromise, or the attackers involved. CISA's entry also lists ransomware use as unknown.CVE-2026-114713: UnrealIRCd UnrealIRCd (UnrealIRCd Improper Neutralization of Delimiters Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
What people are saying
The Hacker News reports that attackers are actively exploiting the flaw and assigns it a CVSS score of 8.6. Its social-media account repeats those claims, but neither item provides victim details or technical evidence of individual attacks in the supplied material.Attackers Exploit UnrealIRCd Flaw That Enables Server-Level Command Injectionthehackernews.com · rssOpen original sourceSee in source listTheHackersNewsx.com · TheHackersNews · xOpen original sourceSee in source list
Evolution
The sequence moved from a CISA catalog entry documenting the vulnerability, required response, and November 16 deadline to subsequent coverage describing active exploitation and urging immediate patching. The later social post summarizes the same outlet's article rather than adding a separate confirmation.CVE-2026-114713: UnrealIRCd UnrealIRCd (UnrealIRCd Improper Neutralization of Delimiters Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source listAttackers Exploit UnrealIRCd Flaw That Enables Server-Level Command Injectionthehackernews.com · rssOpen original sourceSee in source listTheHackersNewsx.com · TheHackersNews · xOpen original sourceSee in source list
Reach
2 independent groups, 2 updates, and 5 engagements.
Technical detail
CVE-2026-114713 is classified as improper neutralization of delimiters. In plain terms, UnrealIRCd does not adequately contain specially structured input before handling it as server-to-server traffic, enabling command injection with server authority under the documented linked-server condition.CVE-2026-114713: UnrealIRCd UnrealIRCd (UnrealIRCd Improper Neutralization of Delimiters Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source list
Sources and evidence
The CISA KEV-derived record is the strongest supplied source for the flaw's mechanics, required action, deadline, and unknown ransomware status. The Hacker News article and its related social post support the public claim of active exploitation and the reported 8.6 severity score, but they form a single reporting chain and do not establish specific victims or campaigns.CVE-2026-114713: UnrealIRCd UnrealIRCd (UnrealIRCd Improper Neutralization of Delimiters Vulnerability)nvd.nist.gov · kevOpen original sourceSee in source listAttackers Exploit UnrealIRCd Flaw That Enables Server-Level Command Injectionthehackernews.com · rssOpen original sourceSee in source listTheHackersNewsx.com · TheHackersNews · xOpen original sourceSee in source list
Sources
- CVE-2026-114713: UnrealIRCd UnrealIRCd (UnrealIRCd Improper Neutralization of Delimiters Vulnerability)nvd.nist.gov · kev
- Attackers Exploit UnrealIRCd Flaw That Enables Server-Level Command Injectionthehackernews.com · rss
- TheHackersNewsx.com · TheHackersNews · x