In 30 seconds
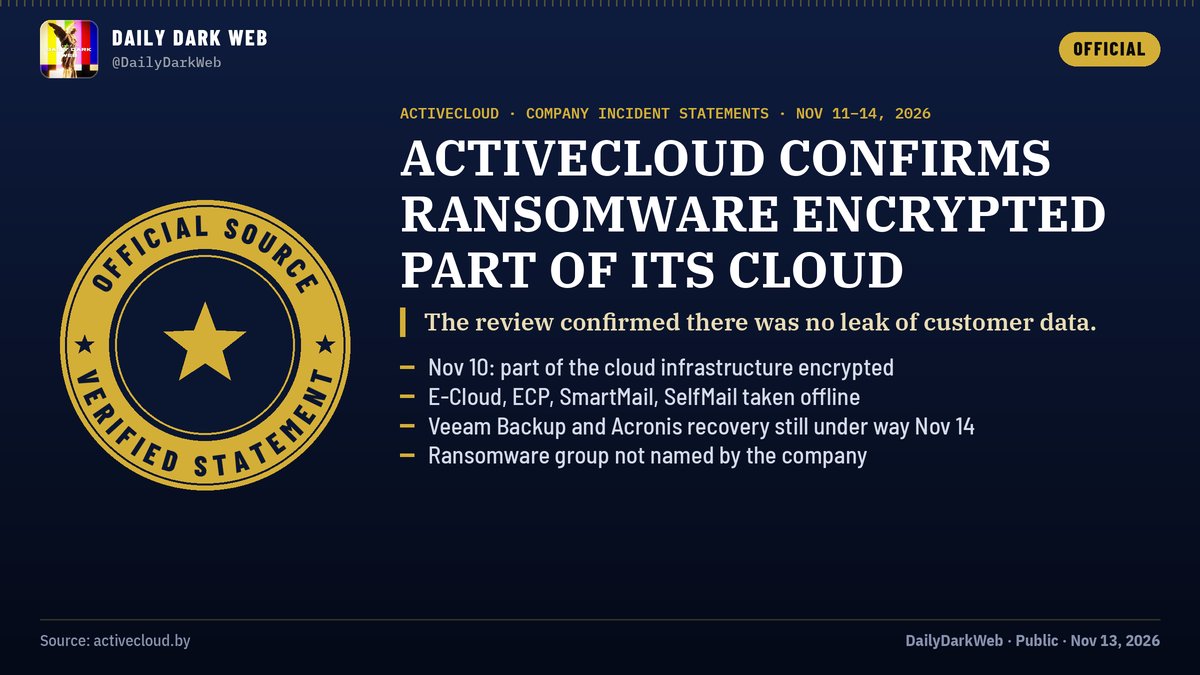
Cloud and hosting provider ActiveCloud says a ransomware attack on November 10, 2026 encrypted part of its cloud infrastructure, and business customers lost access to cloud servers, email and backup services for days. Core services were back by November 12 and 13, while backup recovery was still running on November 14.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listRansomware attack on Belarusian cloud firm disrupts businesses for daystherecord.media · rssOpen original sourceSee in source list
The company says its own early review found no leak of customer data, and as of November 16 no ransomware group had been named for the attack.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
According to ActiveCloud's statements, attackers breached its systems on November 10 and encrypted part of the cloud infrastructure. The Record, reporting on the incident, says the breach left customers unable to access key services for several days.Ransomware attack on Belarusian cloud firm disrupts businesses for daystherecord.media · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The outage took down several products at once: E-Cloud, the E-Cloud Protected (ECP) tier, and the SmartMail and SelfMail email services. Customers could not restore data from backups on their own during the incident, and recovery work using Veeam Backup and Acronis was still under way on November 14.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
On November 13 the company's CEO apologised and called it the most critical attack ActiveCloud has faced. The company has since published a follow-up address from the CEO on its official news page.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listactivecloud.byactivecloud.by · rssOpen original sourceSee in source list
Why it matters
A cloud provider sits upstream of many businesses, so one incident here knocked out computing, email and backups in a single blow. The fact that customers also could not restore from their own backups during the outage shows how a ransomware event at the provider can hurt well beyond the systems that were encrypted.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listRansomware attack on Belarusian cloud firm disrupts businesses for daystherecord.media · rssOpen original sourceSee in source list
The company's no-leak finding is its own early conclusion, not an independent one, and ransomware incidents often see data claims surface later on leak sites. Until a group is named or the data question is checked by outsiders, the possibility of a later leak has not been ruled out.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
ActiveCloud has warned that its support team will contact customers only from the company's official account. Customers should rely on that official channel for updates on the incident and their recovery.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
DailyDarkWeb's analyst note goes further: unsolicited messages referencing this incident are likely phishing attempts, so verify any message against ActiveCloud's official channels before clicking links or handing over credentials, and keep an eye out for a leak-site listing that could confirm or refute the no-leak claim.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
What is established so far: the attack hit on November 10, took multiple services offline, core services returned by November 12 and 13, backup recovery was still continuing on November 14, and the CEO publicly apologised on November 13.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listRansomware attack on Belarusian cloud firm disrupts businesses for daystherecord.media · rssOpen original sourceSee in source list
What is not: the ransomware group and strain remain unidentified, the extent of any data theft is unverified, and there is no word on when full backup recovery will finish. The no-leak line rests solely on the company's own early review.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
ActiveCloud's own statements, issued between November 11 and 14, acknowledged the encryption, the multi-day outage and the ongoing backup recovery. The CEO apologised on November 13 and called it the most critical attack the company has faced, and a further CEO address has been published on the company's site.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listactivecloud.byactivecloud.by · rssOpen original sourceSee in source list
DailyDarkWeb, the threat intelligence account that summarised the statements, describes ActiveCloud as one of Belarus's largest cloud and hosting providers and cautions that the company's early no-leak finding should not be read as independent confirmation.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The timeline starts with the attack on November 10, followed by service failures that knocked E-Cloud, ECP, SmartMail and SelfMail offline for business customers.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Since then the story has shifted to recovery and messaging. Core services returned on November 12 and 13, the CEO apologised on November 13, Veeam and Acronis restoration was still running on November 14, and by November 16 the company had published a post-attack address from its CEO. No ransomware group had been named by that date.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listactivecloud.byactivecloud.by · rssOpen original sourceSee in source list
Reach
2 independent groups, 2 updates, and 0 engagements.
Technical detail
The incident hit named products: E-Cloud and E-Cloud Protected (ECP) for cloud servers, plus SmartMail and SelfMail for email. Backups were caught up in the event too. Customers could not restore data themselves during the outage, and the company was running recovery through Veeam Backup and Acronis as of November 14. No ransomware family or strain has been named.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
This item is built from three pieces of evidence: The Record's news report on the breach and multi-day outage, ActiveCloud's official news page carrying the CEO's post-attack address, and a DailyDarkWeb post that summarises the company's November 11 to 14 statements and adds an analyst note.Ransomware attack on Belarusian cloud firm disrupts businesses for daystherecord.media · rssOpen original sourceSee in source listactivecloud.byactivecloud.by · rssOpen original sourceSee in source listDailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The evidence has clear limits. The CEO address page arrived without body text, the detailed timeline reaches us through DailyDarkWeb's summary of the company statements rather than the statements themselves, and there is no independent verification of the no-leak claim or any attribution to attackers.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listactivecloud.byactivecloud.by · rssOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x
- Ransomware attack on Belarusian cloud firm disrupts businesses for daystherecord.media · rss
- activecloud.byactivecloud.by · rss


