[Single source] Claim: The Gentlemen lists North Macedonia's Erasmus+ agency
The Gentlemen group listed North Macedonia's Erasmus+ agency on its leak site. The post provides no samples, volume, or type of data allegedly stolen. The agency has not publicly confirmed the attack.
In 30 seconds
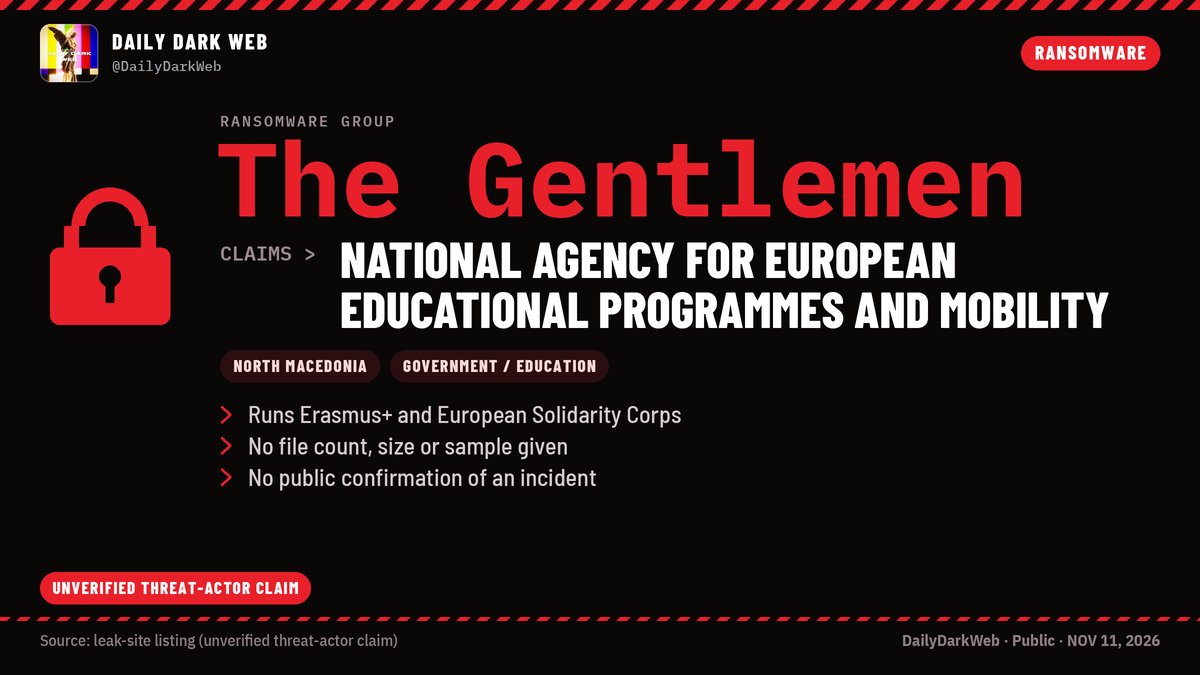
DailyDarkWeb reports that The Gentlemen ransomware group listed North Macedonia's National Agency for European Educational Programmes and Mobility on its leak site. The supplied evidence does not confirm a breach: no stolen-data samples, file count or data volume were presented, and the agency had not publicly confirmed an incident when the post was published.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
According to DailyDarkWeb, the alleged listing names the government body in Skopje that administers Erasmus+ and the European Solidarity Corps in North Macedonia. This establishes a public claim attributed to the ransomware group, not proof that its systems were accessed or data was stolen.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
If the claim proves genuine, the incident could affect sensitive material connected to education programs, including applicant information, participant records and grant files. That potential impact follows from the agency's reported responsibilities, but the evidence does not show that any particular record was exposed.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
Treat the leak-site appearance as an unverified warning rather than a confirmed breach. Students, schools and partner organizations should watch for official agency guidance and be cautious with unexpected messages about Erasmus+, grants or participant accounts, especially while the scope remains unknown.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
The supplied post identifies the alleged victim and says a leak-site listing exists. It also explicitly says the listing contains no sample, file count, data size or description of the purportedly taken records. There is no independent verification or public confirmation from the agency in the evidence provided.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
DailyDarkWeb warns readers not to treat the threat actor's claim as confirmation of a breach. Its analyst note says the agency handles applications, evaluations and participant records for thousands of students, schools and organizations, making a genuine compromise potentially consequential.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The evidence trail currently begins with DailyDarkWeb's report of the leak-site listing. No subsequent agency statement, technical investigation, data sample or independent corroboration is included, so the story has not progressed beyond an attributed ransomware claim in this evidence set.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 0 engagements.
Technical detail
No technical indicators are available in the supplied evidence. The report provides no attack vector, malware behavior, affected systems, intrusion date, encryption status, ransom demand, file inventory or sample that investigators could use to validate the claim.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
The evidence set contains a single DailyDarkWeb post on X, accompanied by an HTTPS-hosted image. It is a secondary report about an alleged threat-actor listing, not a statement from the agency, a forensic report or independently authenticated leaked material.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x


