[Single source] Claim: n0n extortion group lists Vertex Pharmaceuticals on leak site
The n0n data-extortion group has added Vertex Pharmaceuticals to its leak site. The listing is in a pending state, with no data volume, samples or deadline published. Vertex has not confirmed an incident.
In 30 seconds
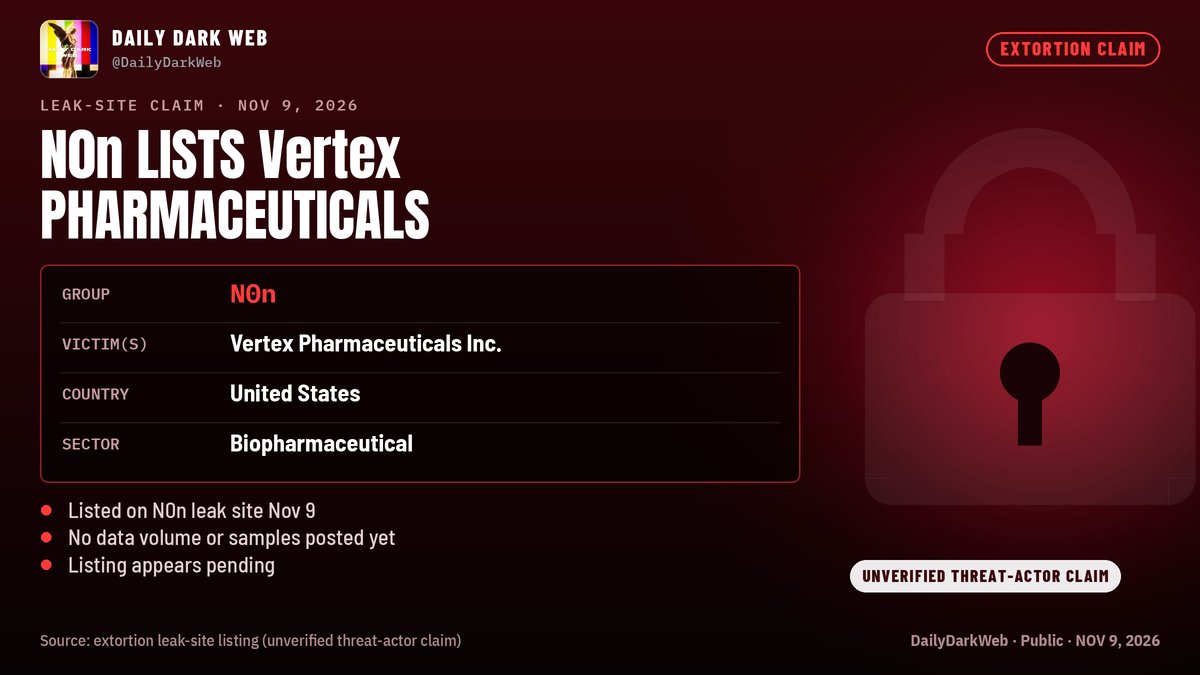
The n0n data-extortion group claims Vertex Pharmaceuticals as its latest target. According to threat-intelligence account DailyDarkWeb, the group added the Boston-based biotech, known for its cystic fibrosis therapies, to its leak site in a pending state, meaning no data volume, no file samples and no deadline have been published. Vertex has not confirmed any incident, and the researcher who surfaced the listing says to treat it as an unverified threat-actor claim, not proof of a breach.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
On November 9, 2026, DailyDarkWeb reported that n0n, a data-extortion crew, listed vrtx.com, Vertex Pharmaceuticals' corporate domain, on its leak site. A leak site is the public storefront where extortion groups pressure victims by threatening to release stolen data.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
As reported, the listing is bare. No data volume, no file samples and no countdown timer appear, and the entry seems to be sitting in a pending state. In other words, the group has named Vertex but has shown nothing to back the name.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
A pending listing usually means the group is holding its cards: name the victim first, publish proof later if the victim does not pay. Read that way, this is the opening move of an extortion attempt, not the middle of one.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
If the claim turns out to be real, the stakes are high. Vertex is the biotech behind leading cystic fibrosis therapies, and the analyst note flags that exposure could include research data, clinical trial records, partner information and employee details.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
That mix raises two separate risks. One is intellectual property theft, painful for a company whose value lives in drug research. The other is regulatory exposure, since clinical trial or patient-adjacent data can trigger notification duties. To be clear, this is scenario analysis about what could be at stake, not evidence of what was actually taken.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
The explicit guidance from the researcher who broke the listing: treat it as an unverified threat-actor claim, not confirmation of a breach. That framing should govern how anyone repeats this story.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Practical next steps for anyone following this: watch Vertex's official channels for a statement, watch the n0n leak site for samples or a deadline, and hold conclusions until one of those appears. Nothing in the current evidence supports saying data was stolen from Vertex.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
What is on the record is thin. One threat-intel account reports a leak-site listing in a pending state with no proof attached, and states that Vertex has not confirmed an incident. The same account says n0n has posted many large US names in bulk this month, which suggests a high-volume claim pattern rather than a carefully staged single operation.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What is unknown is everything that matters: whether Vertex was actually breached, what data if any was taken, when the alleged intrusion happened, and whether n0n will escalate with samples or a deadline. No second source in this batch corroborates the listing independently.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
DailyDarkWeb, the account that surfaced the listing, put it bluntly: treat this as an unverified threat-actor claim, NOT confirmation of a breach. The same post notes that the listing gives no data volume, samples or deadline, and that Vertex has not confirmed an incident.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The same analyst note sketches the downside scenario, warning that if the claim is real, exposure could span research, clinical trial, partner and employee data, and raises both IP theft and regulatory concerns. That is the analyst's own risk framing, offered alongside the caution against treating the listing as fact.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The public timeline has a single marker so far: the DailyDarkWeb post on November 9, 2026 reporting the pending listing. This batch contains no earlier reporting on Vertex and n0n, no prior claims by the group against the company, and no follow-up developments.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The next checkpoints are mechanical. Either n0n posts proof or a deadline, or the listing sits pending indefinitely, or it quietly disappears. Each outcome would read differently: escalation lends the claim weight, silence or removal tends to undercut it.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 0 engagements.
Technical detail
The reported listing targets vrtx.com, Vertex's corporate domain. As described, the entry carries no data volume figure, no file samples and no deadline timer, which is the typical shape of a first-stage extortion listing.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
In the standard extortion playbook, a pending listing functions as leverage: the group names the victim and waits, with future publication as the implied threat. The absence of samples is the key technical gap, because it means nobody outside n0n can currently verify that any Vertex data exists.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
This story rests on a single source: a November 9, 2026 post by DailyDarkWeb on X, which includes an image credited to the account alongside the claim. No corporate statement from Vertex, no regulatory filing and no second intelligence source appears in the evidence batch.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
With one source and zero proof published, the responsible confidence level is low. The claim is plausible enough to monitor, but nothing here lifts it above an unverified threat-actor assertion, and any future update should hinge on new evidence: leaked samples, a deadline, or word from Vertex itself.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x


