[Single source] MortemTeam claims second Canelones government data leak
MortemTeam claims it released the second part of a leak from Uruguay's Canelones departmental government. The alleged data includes names, addresses, and phone numbers. The cited count ranges from over 80,000 to 700,000 records and remains unconfirmed.
In 30 seconds
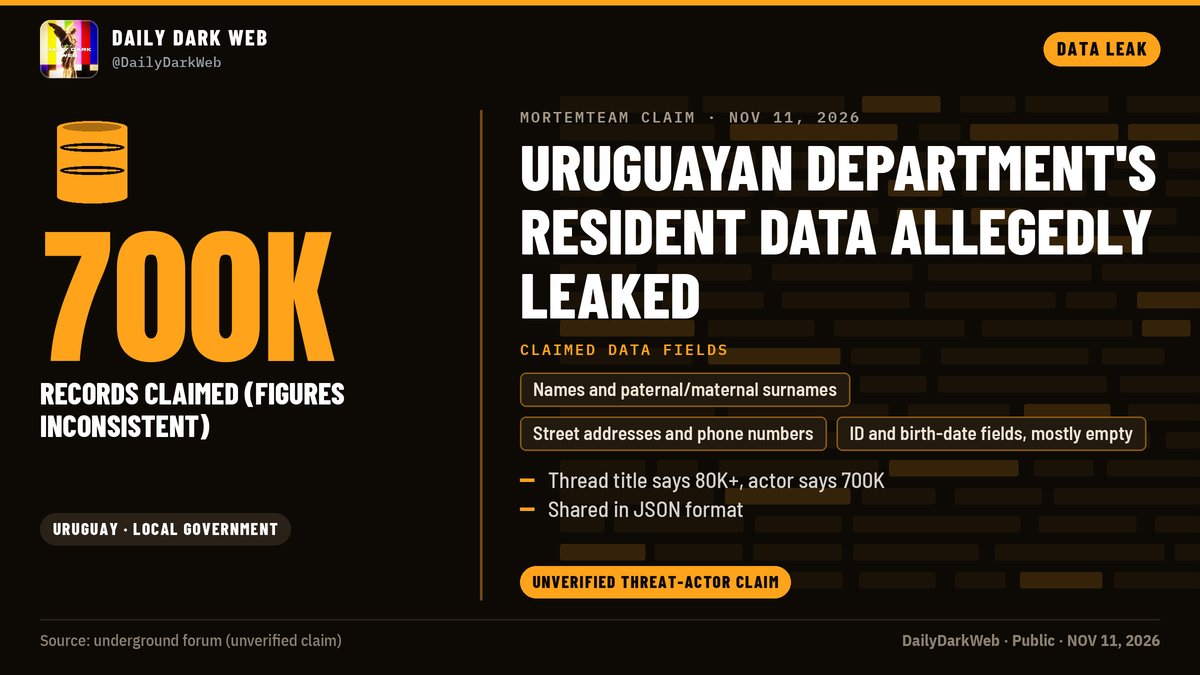
MortemTeam claims it released a second batch of data connected to the Canelones departmental government in Uruguay. The claim is unverified, the reported volume ranges from more than 80,000 to 700,000 records, and there is no evidence here confirming that government systems were breached.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
DailyDarkWeb reported that a threat actor posting for MortemTeam described the release as “Part II” of a campaign targeting Uruguay's government. The purported material contains business and individual entries with names, addresses and phone numbers.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
If the information is authentic and current, combining names with addresses and phone numbers could make phishing, impersonation and fraud attempts more convincing, even without complete national identification numbers or birth dates.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
People and organizations connected to Canelones should treat unexpected messages that use personal details with caution, verify requests through a separate official channel and avoid sharing credentials or payment information. These are precautions based on the reported exposure, not proof that any particular person appears in the files.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
The available report does not establish where the data came from, whether it is authentic, whether it was recently obtained or whether Canelones government systems were accessed. DailyDarkWeb also said it found no public statement from the Intendencia de Canelones.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
DailyDarkWeb explicitly characterized the episode as an unverified threat actor claim rather than confirmation of a breach. Its analyst note suggested the material may be directory-style contact data that was aggregated or scraped, citing inconsistent totals, reused target details and mostly empty identity fields.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The actor reportedly framed this publication as the second installment following earlier warnings against Uruguay's government. The same report says MortemTeam also promoted claims involving an Argentine municipality and had previously named Argentina's central bank and Peru's tax authority, with the latter reportedly denying an intrusion.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 0 engagements.
Technical detail
According to DailyDarkWeb, the entries were shared in JSON format and included paternal and maternal surnames, street addresses and phone numbers. Fields for national identification numbers and dates of birth were present but largely empty in the sample it described.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
The supplied evidence consists of one DailyDarkWeb post on X and its attached image. It includes descriptions of a posted sample and the actor's statements, but no primary dataset, forensic findings, independent validation or official response from Canelones.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x


