In 30 seconds
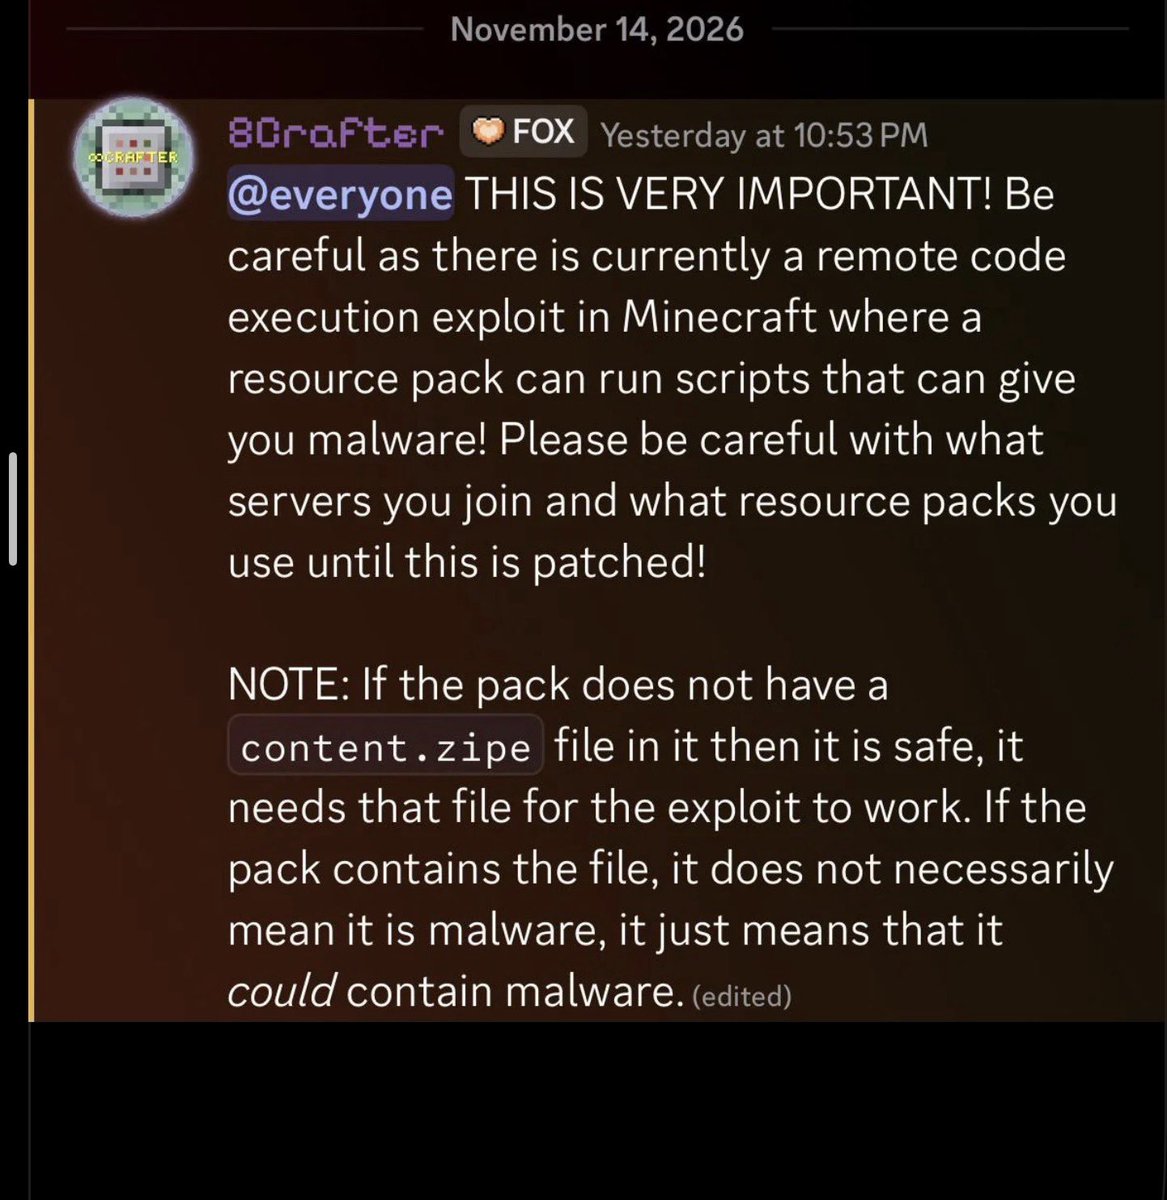
A public post claims Minecraft Bedrock shipped with a serious security flaw: malicious resource packs, the add-on files players use to change how the game looks, could allegedly delete saved worlds, read players' IP addresses, tamper with friend lists and download malware onto Windows machines. The same post says Mojang has released version 26.65, which appears to fix the issue. Java Edition was reportedly not affected.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
What happened
The report comes from the X account Pirat_Nation. It places the problem inside Ore UI, the framework Bedrock uses to draw its menus and interface. Once a crafted pack was loaded, the post alleges, it could use that layer to act outside the game's normal limits: destroying worlds, harvesting IP addresses, editing the friend list and fetching extra malicious software on Windows.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
On scope and remedy, the post says every Bedrock platform was exposed, PC, console and mobile alike, while Java Edition stayed out of the blast radius. As for the fix, the wording is hedged: version 26.65 appears to close the hole, which is softer language than a confirmed patch.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Why it matters
Resource packs are among the most popular ways to customize Minecraft, and the game's audience includes a lot of younger players, so a path that turns a cosmetic download into system-level trouble deserves attention. A deleted world can erase hundreds of hours of play, and an IP address is a small but real piece of someone's online footprint that can enable targeted harassment or further attacks.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
What to do
If you play Bedrock on any device, the practical step reported here is to update to version 26.65 or later before installing anything new. Keep in mind the fix is attested only by the circulating post, so treat the version number as the reported remedy rather than a vendor-confirmed one.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
While confirmation is pending, standard hygiene still applies: download packs only from sources you trust, and check what younger players in the house are installing. The described attack rides on a pack being loaded in the first place.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Confirmed and still uncertain
What the evidence supports so far is narrow: one public post describing the flaw, its alleged effects and a patch. What it does not support is everything else. This batch holds no Mojang or Microsoft advisory, no CVE identifier, no researcher writeup, no exploit code and no sign of real-world victims.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Even the fix comes with soft language, since the post says 26.65 appears to fix the issue. That leaves open the questions a vendor advisory would normally answer: whether the patch covers every platform at once, whether the flaw was exploited in the wild before the update, and who discovered it in the first place.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
What people are saying
The only voice in this batch is Pirat_Nation, whose post states the case bluntly: Bedrock had a serious security flaw, malicious packs could exploit Ore UI, and the consequences ranged from deleted worlds to malware on Windows. The account also asserts flatly that Java Edition was unaffected, one of the few claims in the post delivered without a hedge.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Evolution
The public record here starts on November 17, 2026, when the Pirat_Nation post went up describing the Ore UI flaw and pointing to version 26.65 as the remedy.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Because the warning already references the patch, the sequence reads as fix first, disclosure second. With a single source, though, there is no way to tell when the flaw was found, who found it, or whether Mojang was told privately before the update shipped.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 858 engagements.
Technical detail
On mechanics the report is thin but pointed about targets. Ore UI is Bedrock's in-house interface system, the layer that renders menus and on-screen elements, and it is what the malicious packs allegedly abused. The claimed effects are world deletion, IP address access, friend list manipulation and a download stage for malware that the post limits to Windows. Missing entirely: how the exploit chain works, whether a victim merely installs the pack or must take further steps, and any technical identifier such as a CVE number.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Sources and evidence
The evidence base is a single item: a public post by Pirat_Nation on X, published November 17, 2026, with an attached screenshot. It is a discussion post, not a vendor advisory or a researcher's technical writeup, and this batch contains no corroboration from Mojang, Microsoft or an independent security firm. Every claim in this story traces back to that one thread and should be weighed accordingly.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Sources
- Pirat_Nationx.com · Pirat_Nation · x