In 30 seconds
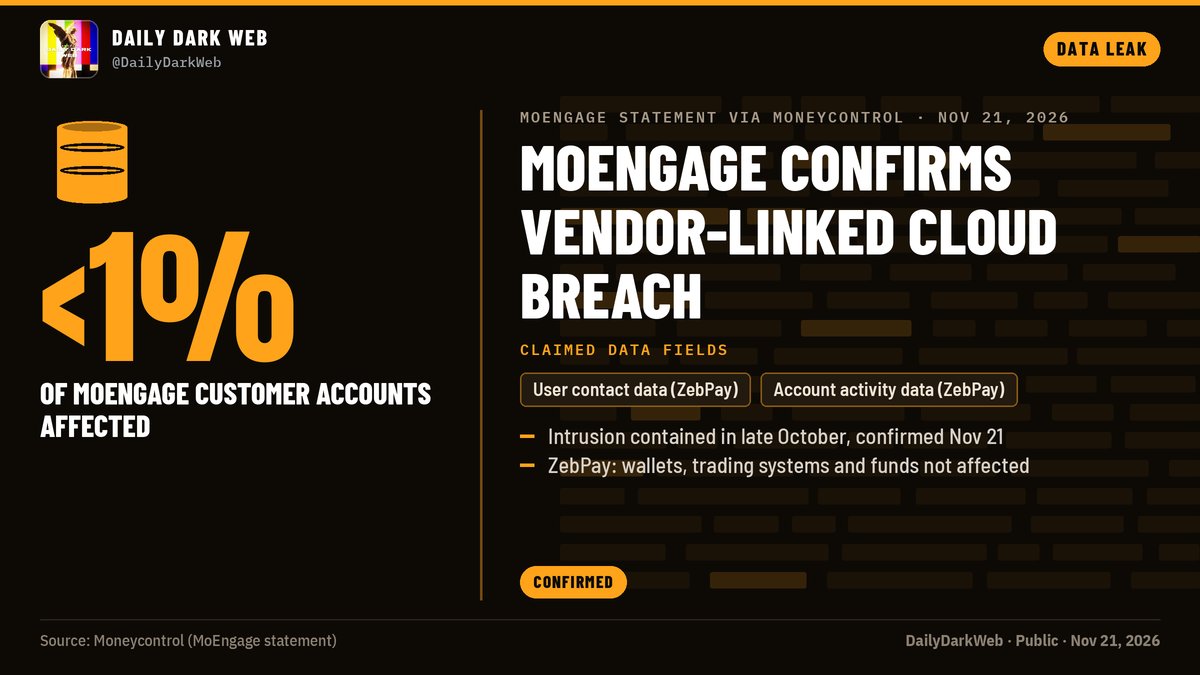
DailyDarkWeb reports that MoEngage confirmed a compromised vendor account led to a breach of its cloud environment. The post says fewer than 1% of MoEngage customer accounts were affected and that some ZebPay users had contact and account activity data exposed, while wallets and trading systems were unaffected.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
The reported chain begins with the compromise of a vendor account, followed by access to MoEngage's cloud environment. ZebPay then reportedly disclosed exposure involving some users, connecting the incident at a service provider to data belonging to a customer of that provider.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
The incident illustrates the potential reach of third-party access: one compromised vendor credential can become a route into a cloud service and affect organizations that depend on it. In this case, the reported effects reached ZebPay user information even though ZebPay's core financial systems were said to be unaffected.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
The supplied evidence includes no remediation instructions. Potentially affected customers should therefore look for direct notices from MoEngage or ZebPay, remain cautious about messages using exposed contact or activity details, and avoid treating unsolicited requests as legitimate solely because they contain familiar account information.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
The report identifies the alleged entry point, gives a relative impact estimate and distinguishes exposed ZebPay data from unaffected systems. It does not identify the vendor, provide an exact account count, describe the specific activity fields exposed, state when access began or ended, or explain how the vendor account was compromised.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
DailyDarkWeb says MoEngage confirmed the vendor-account compromise and the impact to fewer than 1% of customer accounts. The same post attributes to ZebPay the statement that some contact and account activity data was exposed, but wallets and trading systems were not affected.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The available account presents a causal sequence rather than a detailed timeline: a vendor account was reportedly compromised, MoEngage's cloud environment was breached, and downstream exposure was later described for some ZebPay users. No dated milestones for discovery, containment or notification are included.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 0 engagements.
Technical detail
The evidence describes a compromised vendor account as the route into a cloud environment, but provides no authentication logs, cloud provider, permissions, exploited vulnerability or persistence method. It also reports a boundary around ZebPay's impact: contact and account activity data were exposed, while wallets and trading systems were not.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
The evidence batch contains a DailyDarkWeb post with the substantive claims and an RSS record pointing to a Moneycontrol article. The RSS record supplies a canonical URL and publication metadata but no title or article body, so it cannot independently verify the incident details provided in the post.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source listmoneycontrol.commoneycontrol.com · rssOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x
- moneycontrol.commoneycontrol.com · rss