What happened
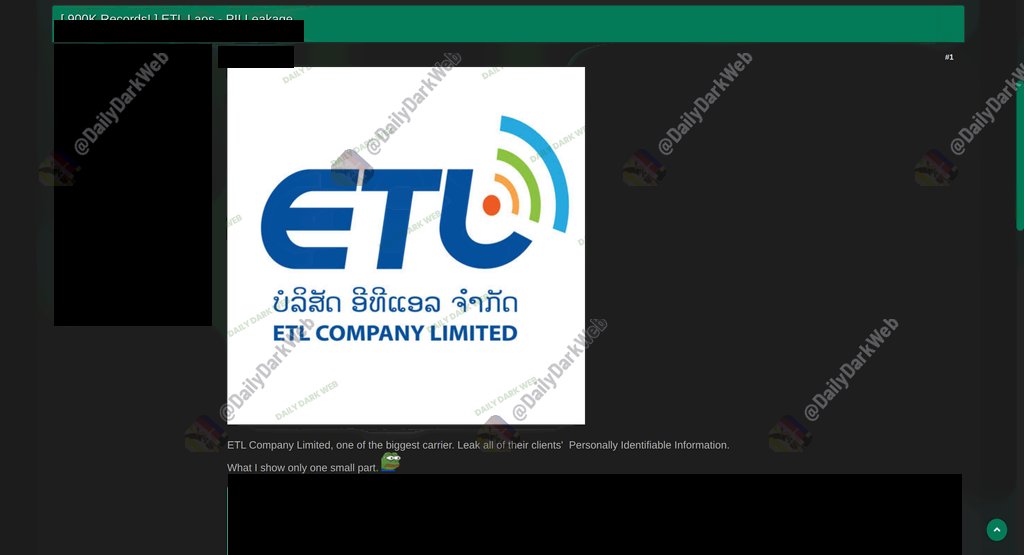
The story begins with a listing on an underground forum. A threat actor, the usual term for someone acting with malicious intent, claims to have leaked customer data belonging to ETL Company Limited, a major player in Laos telecom.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
According to that listing, as surfaced by the monitoring account DailyDarkWeb, the claimed haul covers roughly 900,000 customer records, with fields such as full names, phone numbers, addresses and other personal identifiers. That is the full extent of what is on the record so far.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
The analyst note attached to the reporting makes the same point: telecom subscriber data linked to names and addresses is known fuel for these fraud chains. That risk assessment is an inference, not a confirmed outcome of this particular listing.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
Treat any unexpected call or text that already knows your name and number with suspicion, even if it looks like it comes from your carrier. The claimed dataset is precisely the kind that makes such approaches look legitimate.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Until ETL or an independent party confirms the breach, standard hygiene is the sensible response: never share one-time codes, and verify anything urgent by calling the carrier's official number yourself.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
What is observable: a forum listing making this claim exists, and it was reported publicly by DailyDarkWeb on X on November 17, 2026. The post itself flags the claim as unverified and notes the carrier has not commented.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What is unknown: whether the data is genuine, where it came from, how current it is, and whether anyone has already bought it. No sample, no proof and no breach method have been made public, so authenticity currently rests entirely on the seller's word.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
Only one voice is public so far: DailyDarkWeb, an account that tracks underground activity, reported the listing and attached an explicit warning that it is unverified. ETL itself has stayed silent, so there is no company side of the story yet.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
This story is at its very first checkpoint. It exists as a single forum listing surfaced in one report, with no earlier public signs of an ETL breach, no follow-up posts and no carrier response to track yet. The next real development would be confirmation or denial from ETL, or independent verification of the data.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 0 engagements.
Technical detail
The listing spells out the fields on offer: full names, phone numbers, addresses and what it calls other personal identifiers. In practice that is identity-linking data rather than passwords or payment card numbers, which points more toward fraud and impersonation than direct account takeover of the carrier's systems.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
No technical proof has been shown publicly. There is no sample dataset, no database structure and no explanation of how the data was supposedly obtained, so there is nothing yet for researchers to independently check.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
The entire public record at this moment is one post by DailyDarkWeb on X, published November 17, 2026, which includes a screenshot of the forum listing and an analyst note marking the claim as unverified. It is a secondary source reporting a primary claim, and until ETL comments or the data is independently examined, it should be read as exactly that.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x


