In 30 seconds
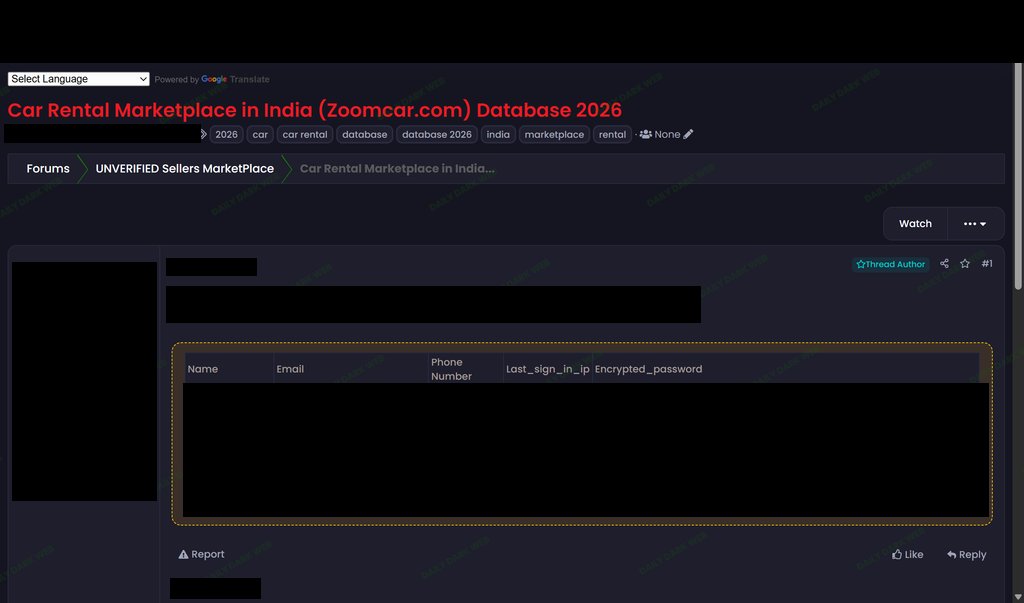
A listing on an underground forum is offering what it calls a 2026 user database for Zoomcar, the Indian car-sharing and rental marketplace. The seller claims the data includes names, emails, phone numbers, bcrypt password hashes, last sign-in IP addresses, home addresses, GPS coordinates, and account status with timestamps. None of it has been verified.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The monitoring account that surfaced the listing calls it an unverified claim from an unverified seller section, and says it may simply recycle data from a breach Zoomcar disclosed in 2025, which affected roughly 8.4 million users. Even recycled, phone numbers and home addresses give scammers material for phishing and SIM-swap attempts, where a thief hijacks your phone number to intercept one-time codes.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
The claim went public on November 17, 2026, when DailyDarkWeb, an account that tracks underground forum activity, posted about the listing on X along with a screenshot.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The listing claims to sell a 2026 user database from Zoomcar, an Indian car-sharing and rental marketplace. The advertised fields are names, emails, phone numbers, bcrypt password hashes, last sign-in IP addresses, home addresses, GPS coordinates, and account status and timestamps.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The analyst note attached to the post adds the backdrop: Zoomcar disclosed a breach affecting about 8.4 million users in 2025, so the listing may be recycled data from that incident. As of the post, Zoomcar had not commented.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
If it is recycled 2025 data, the alert level drops but does not vanish. Old breach data circulates for years, and bcrypt hashes, while slow and expensive to crack, still reward patient attackers who target weak passwords.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
For Zoomcar users the practical steps are simple. Change your password, ideally to one you use nowhere else, and switch two-factor authentication to an app or passkey rather than SMS, because SMS codes are exactly what SIM-swap thieves intercept.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Stay alert to contact that leaks personal detail. A caller who knows your name, address, or past activity is not automatically legitimate, and no real support agent will ask you to read out a one-time code.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
What is on the record: a forum listing exists, it was publicly flagged by DailyDarkWeb on November 17, 2026 with a screenshot, and the account says Zoomcar had not commented at posting time.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What is alleged: every specific about the database itself, including the 2026 date, the field list, and whether the seller actually holds anything. The 2025 breach affecting about 8.4 million users is likewise cited only in the analyst note.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What nobody knows yet: whether the data is fresh, recycled, or fabricated, how many people it would cover, and whether Zoomcar will investigate or respond.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
The only public voice so far is DailyDarkWeb, the account that surfaced the listing. Its own read is cautious: unverified claim, unverified seller section, possible recycled data from 2025, yet phone numbers and addresses remain useful for phishing and SIM-swap attempts. Zoomcar itself has said nothing publicly, according to the post.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The reference point is 2025, when, according to the analyst note, Zoomcar disclosed a breach affecting about 8.4 million users.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
This listing does not yet establish a new breach. The most economical reading offered so far is an old dataset resold with a 2026 label, and the picture would only change if Zoomcar confirms an incident, researchers examine a data sample, or both.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 1 engagements.
Technical detail
The advertised fields: names, emails, phone numbers, bcrypt password hashes, last sign-in IP addresses, home addresses, GPS coordinates, and account status and timestamps.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Two details stand out. Bcrypt is a deliberately slow password hashing algorithm, so cracking strong passwords is costly, though weak ones remain vulnerable. The location cluster is the sharper worry: last sign-in IPs, home addresses, and GPS coordinates together would paint an unusually precise picture of users' movements if the data is genuine.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
This story currently rests on a single source: a November 17, 2026 post by DailyDarkWeb on X, which includes an image of the purported forum listing and an analyst note.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
The evidence has obvious limits. One indirect account of the listing, no data sample, no corroboration from other researchers, and no company response. Every specific claim about the database should be treated as unverified until Zoomcar comments or the data is independently examined.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x