In 30 seconds
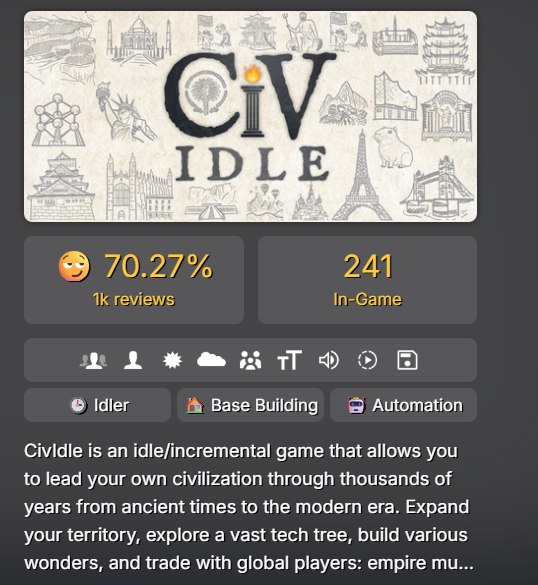
A Steam game became a malware delivery channel, according to a report citing the CivIdle developer. The developer says an attacker exploited a flaw in the game's chat system on November 15: rigged private messages injected scripts that could ultimately install a Trojan, which is malware disguised as something harmless, on Windows players' computers.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
The reported response came fast and in layers: direct messages switched off, a server-side fix deployed, and a client update called Build 1018 released. The developer also flagged specific files to look for, including q.exe in the game folder and p.bat in C:\Users\Public.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
What happened
The incident dates to November 15 in the developer's account as relayed by the report. An attacker sent specially crafted private messages through CivIdle's chat system, abusing a vulnerability to inject malicious scripts that could ultimately install malware on players' computers.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Containment followed, per the same account. The developer disabled direct messages, deployed a fix on the server side so the injection route would close without players needing to act, and shipped an additional client update numbered Build 1018.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Two boundary details round out the reported picture: the attack was reportedly a carefully planned attempt to bypass chat restrictions, and Linux and macOS players were not affected, according to the developer.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Why it matters
The case is a reminder that a game with a chat system is also a messaging platform, and a flaw in that chat can turn casual playtime into a malware infection risk. Players tend to let their guard down for messages that arrive inside a game they already trust.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
It also shows why concrete indicators matter. By naming specific files such as q.exe and p.bat, the developer gave players a practical way to check their own machines instead of guessing whether they were hit.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
What to do
If you play CivIdle on Windows, follow the developer's guidance as reported: update the game to Build 1018, then check the game folder for q.exe and look for p.bat in C:\Users\Public. Finding either file is the developer's sign of a possible infection.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
The server-side fix is reported to close the injection route on its own, but the client update and the file check are still worth doing, since the report does not present the two measures as interchangeable.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Confirmed and still uncertain
What the report establishes, all attributed to the developer: the chat system flaw, the November 15 date, the private-message injection route, Windows as the affected platform, the DM shutdown, the server fix, Build 1018, and the two indicator files.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
What it does not establish: how many players received the malicious messages or were infected, what the malware was built to do, who was behind it, and whether anything was taken. The batch carries no victim count and no independent confirmation of the developer's account.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
What people are saying
The only voice in this batch is Pirat_Nation, an X account that published the consolidated report and framed it starkly: a Steam game used to spread a Trojan targeting Windows players. Notably, every key fact in the post is attributed to the game's developer rather than to the account's own testing.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Evolution
The public record here arrives already wrapped up. The single report in this batch was published after the developer had confirmed the attack and shipped fixes, so the story surfaces as flaw found, chat closed, patch out, with no visible interim stage of attacker messages spreading or players complaining. That snapshot shape has a cost: without the developer's original posts or a security writeup, the whole timeline rests on one secondary account.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 471 engagements.
Technical detail
The mechanism, as described, is a chat injection chain. Specially crafted private messages carried hostile content through the chat system, the vulnerability allowed those messages to inject scripts on the receiving end, and the scripts could ultimately install malware on Windows machines. The report adds that the scheme was reportedly a carefully planned attempt to bypass chat restrictions, which implies some filtering existed for the attacker to work around.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
For players inspecting their systems, the named indicators of compromise are q.exe in the game folder and p.bat in C:\Users\Public, and the platform scope is Windows only, with Linux and macOS reported unaffected.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Sources and evidence
This item rests on one source: a public X post by Pirat_Nation that summarizes the CivIdle developer's statements and includes a screenshot. No developer post, patch notes, vendor analysis, or player testimony appears in the batch.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Because of that single, secondhand chain of custody, every factual claim above should be read as the developer's account relayed by one reporter, not as independently verified fact. Corroboration from the developer's own channels or a security vendor would materially strengthen the story.Pirat_Nationx.com · Pirat_Nation · xOpen original sourceSee in source list
Sources
- Pirat_Nationx.com · Pirat_Nation · x