In 30 seconds
A threat actor claims to have hacked Seaker, a Philippine job platform for seafarers, and downloaded all of its data. According to the claim, relayed by the monitoring account DailyDarkWeb, the haul covers 54,167 people and includes passport details, seaman's documents, personal photos, full profiles, and even admin dashboard access. Nothing here is confirmed, and Seaker has not commented. The practical takeaway for Filipino seafarers is simple: be extra careful with recruitment offers, because leaked passport scans make job and visa scams far more convincing.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
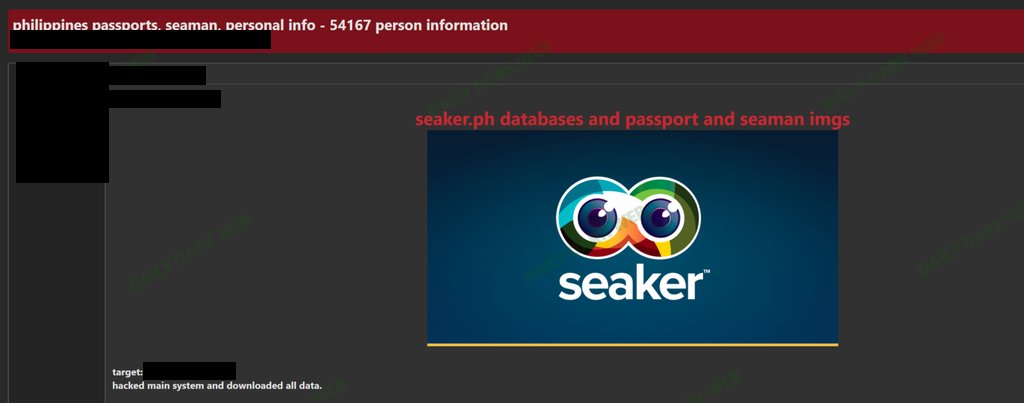
The claim went public through a post from DailyDarkWeb, an account that tracks breach claims and dark web activity. The post reports what a threat actor is alleging, pairs it with a screenshot, and adds an analyst note stating plainly that the claim is unverified and that Seaker has not commented.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
In the threat actor's own telling, the actor hacked the platform and pulled its entire dataset. The claimed inventory includes records on 54,167 seafarers, passport details, seaman's documents, personal photos, full profiles, and access to the admin dashboard, which is the control panel staff use to run the site.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
The analyst note attached to the report spells out the human stakes. Filipino seafarers are frequent targets of fake recruitment and visa scams, and passport scans make those scams far more convincing. A fraudster who can quote your real passport number and show your own photo starts the conversation with a level of credibility that a cold call never has.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
There is also a longer tail of risk. Documents like passports and seaman's books anchor many kinds of identity verification, so if this data is real and starts circulating, the fallout would likely look like phishing messages, fake job offers, and impersonation attempts rather than one dramatic incident.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
If you are registered on Seaker, raise your guard against unexpected recruitment contact. Be especially wary of any offer that asks for fees, extra copies of your documents, or an urgent decision, and verify the recruiter through official manning agency or company channels before sharing anything.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Watch for one specific red flag: messages that quote your actual passport or seaman's book details back at you. That specificity is exactly what a leak like the one claimed would enable, and it matters more than a convincing logo or job title.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
On the claimed side of the ledger: a full database download, 54,167 affected people, passport details, seaman's documents, personal photos, full profiles, and admin dashboard access. Every one of those specifics comes from the threat actor's own post.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
On the unknown side sits almost everything else. There is no confirmation that a breach happened, no sample of the purported data, no identified actor, and no statement from Seaker. The company's silence means affected users currently have no official channel of information.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
One voice dominates so far: DailyDarkWeb, which reported the claim while explicitly labeling it unverified and noting that Seaker has not commented. Seaker itself has said nothing publicly, and no researcher or affected user has stepped forward to corroborate the story.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
This story is at its starting point. A single post made the claim public, and the current record contains no follow-up: no leaked samples, no company response, no attribution. The next signals to watch are a Seaker statement, the appearance of sample data, or corroboration from independent researchers.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 1 engagements.
Technical detail
The claim describes a complete database download rather than a partial scrape. The listed data types are passport details, seaman's documents, personal photos, and full profiles, and the actor also claims admin dashboard access on top of the data itself.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
That admin access detail, if true, would point to a deeper compromise of the platform rather than an exposed endpoint or a single compromised account. It remains a claim within a claim, with nothing technical published yet to support it.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
The entire story currently rests on one source: a post by DailyDarkWeb on X, which includes a screenshot and an analyst note marking the claim as unverified. There is no company statement, no leak sample, and no third-party confirmation in the evidence so far. Until any of that changes, treat the numbers and the data types as the threat actor's own account, not established fact.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x


