In 30 seconds
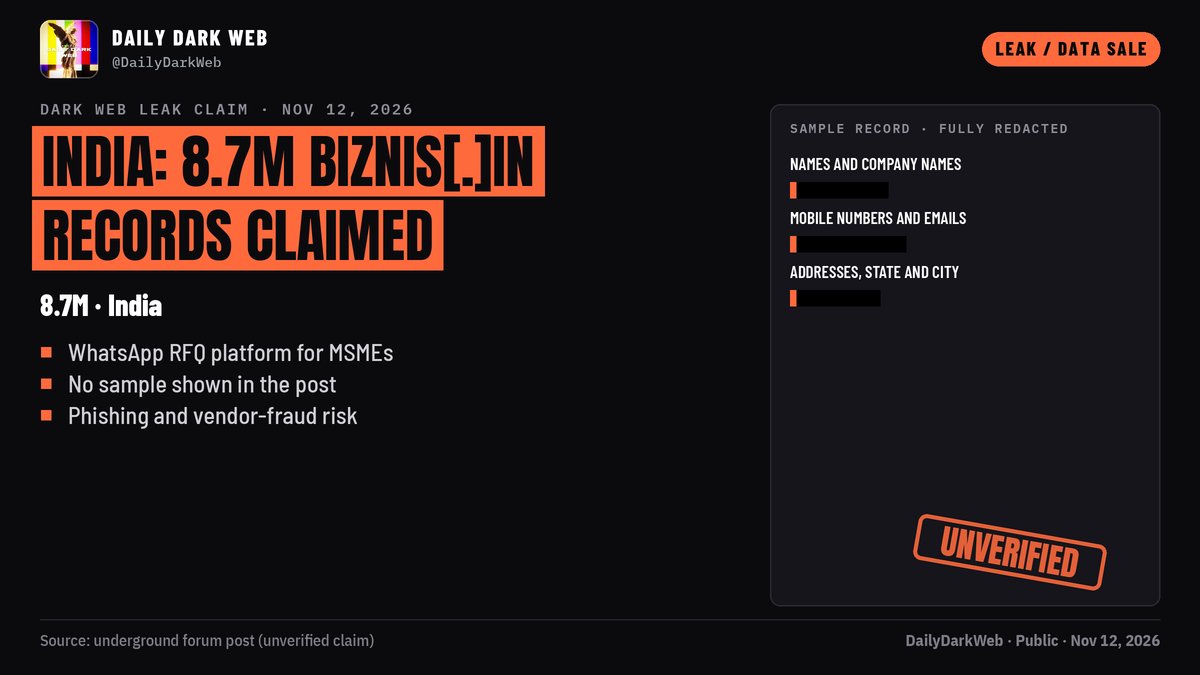
DailyDarkWeb reports that an underground forum actor is offering a database allegedly taken from Biznis.in, with a claimed 8,761,191 records. The report explicitly says the claim is unverified and provides neither data samples nor intrusion details.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What happened
According to the post, the actor described the material as a Biznis.in database containing business and personal contact information. No evidence in the supplied material independently establishes that the records came from Biznis.in or that its systems were breached.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Why it matters
If authentic, combining company details with direct contact information and product interests could make targeted WhatsApp or SMS phishing, fake purchase requests and vendor impersonation more convincing for Indian small and medium-sized businesses.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What to do
Treat the offer as an unverified warning, not a confirmed breach. Biznis.in and potentially affected businesses should first seek a representative sample and validate it against records they already control, while watching for unusual WhatsApp messages, purchase requests and changes to vendor payment details.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Confirmed and still uncertain
What is known is limited to DailyDarkWeb's account of the forum offer and its stated record count. The supplied evidence does not reveal a sample, the forum listing itself, when the data was collected, how access was allegedly obtained, whether records are current, or whether Biznis.in has confirmed any incident.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
What people are saying
DailyDarkWeb labels the report an unverified threat-actor claim and stresses that it is not confirmation of a breach. Its analyst note says the alleged mix of personal and business data would be useful for phishing and impersonation fraud if genuine.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Evolution
The available timeline begins with the reported underground-forum offer and ends with DailyDarkWeb publicizing it. No later verification, company response, independent analysis or disclosure of samples appears in the supplied evidence, so the picture has not advanced beyond the initial allegation.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 0 engagements.
Technical detail
The alleged fields include full names, company names, mobile numbers, email addresses, postal addresses, state and city, user type, and products handled by each business. The evidence provides no file structure, sample rows, timestamps, database metadata or technical indicators that could authenticate the dataset or explain its origin.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources and evidence
The evidence base contains one public X post from DailyDarkWeb, including an HTTPS-hosted image. It is a secondary account of an alleged underground-forum listing, and the post itself acknowledges that no sample or intrusion details were shown. The central claim therefore remains uncorroborated.DailyDarkWebx.com · DailyDarkWeb · xOpen original sourceSee in source list
Sources
- DailyDarkWebx.com · DailyDarkWeb · x


