In 30 seconds
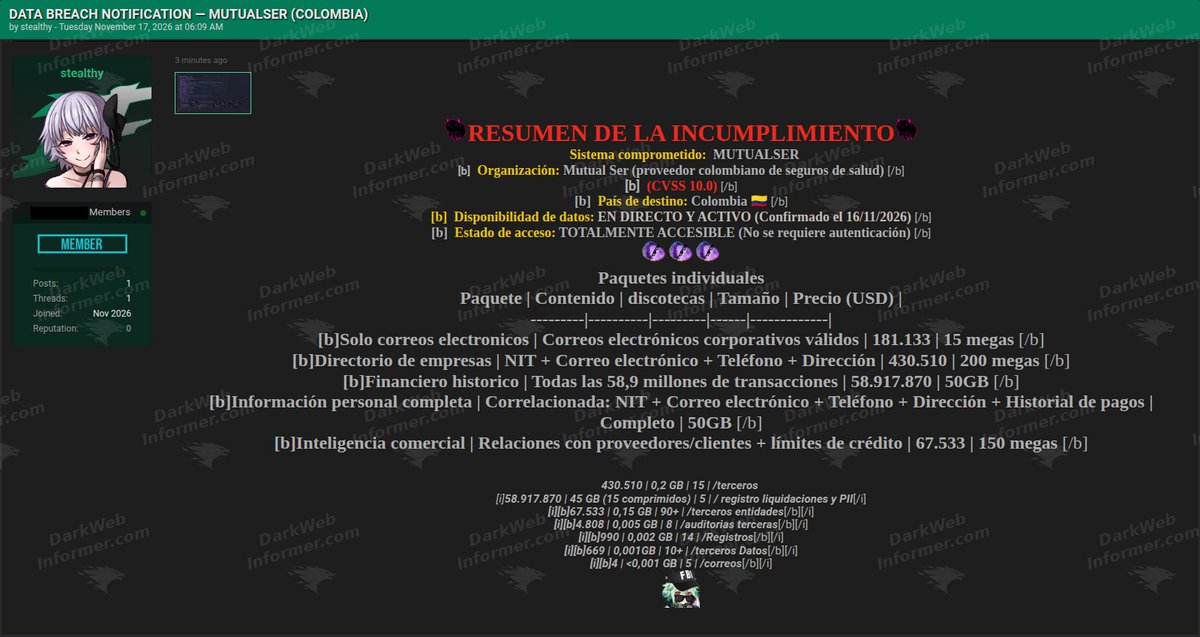
A threat actor going by the name "stealthy" is advertising a claimed breach of Mutual Ser, a Colombian health insurance provider, and says it is selling 58.9 million transaction records plus 430 thousand directory entries, headlined by a 50 GB financial archive. The offer surfaced on November 17, 2026 through a post from DarkWebInformer, an account that tracks criminal markets. Nothing is confirmed: Mutual Ser has not responded, and the only evidence so far is the actor's own sales pitch.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
The actor claims the haul includes 181,133 corporate email addresses, company tax IDs, phone numbers and addresses, historical payment records, personal information tied to financial histories, and supplier relationships with credit limits. All of those contents exist only as claims for now.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
What happened
The story became public on November 17, 2026, when DarkWebInformer published a summary of an offer it had seen from an actor calling itself "stealthy". According to the post, the actor says it compromised Mutual Ser and is now advertising sensitive corporate, financial and personal information for sale.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
The advertised package is oddly specific: 58.9 million transaction records, 430 thousand directory entries, and individual datasets sold separately, with a 50 GB financial archive as the flagship item. The actor also claims the underlying data remains accessible without authentication, which in plain terms means no password would be needed to reach it.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
DarkWebInformer attached its own caution label, stating that the claim is currently unverified. Within the evidence available, there is no confirmation from Mutual Ser, no sample data, and no second source.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Why it matters
If the claim turns out to be real, the material is a strong base for fraud. Health insurers sit on exactly the mix criminals like: identities, payment histories, corporate contacts and supplier details that can make a scam message look legitimate.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
The 181 thousand corporate email addresses stand out. Lists like that typically feed business email compromise, where attackers impersonate a supplier or an executive to redirect payments, and the risk grows when credit limits and supplier relationships travel in the same package.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Customers of a health insurer are not the usual corporate targets, so personal information linked to financial histories could resurface in phishing that cites real payments or coverage, making the lures harder to spot.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
What to do
If you are a Mutual Ser customer or partner, treat any unexpected message that references your policy, payments or supplier account as suspicious, and verify through official channels before acting on it.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
On the company side, the actor's claim that the data is accessible without authentication points to a concrete first step: audit exposed endpoints, require authentication everywhere, and check whether the advertised record counts match anything real in their systems.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Keep an eye on accounts and statements for unusual activity, and be extra careful with payment change requests or invoices that mention Mutual Ser, since supplier and credit details are part of the claimed package.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Confirmed and still uncertain
Known: a public sales claim exists, with a named actor, a named victim and precise record counts, published by a monitoring account on November 17, 2026, and that account itself calls the claim unverified.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Unknown: whether the breach happened at all, whether the data is genuine, how old it is, and how the actor supposedly obtained it. Also unknown: whether Mutual Ser has been contacted, whether samples have circulated among buyers, and whether any regulator is involved. The single source in this batch cannot answer any of that.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
What people are saying
The only voice in the evidence so far is DarkWebInformer, which reported the offer in monitor style: victim, sector, actor, record counts, and a closing note that the claim is unverified.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
The actor "stealthy" speaks only through the advertised listing as relayed by that post. Mutual Ser has said nothing that appears in this batch.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Evolution
This story is at its first step. As of this batch there is one public post, no visible history for "stealthy" here, no confirmation, no denial, and no observed release of samples.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
The beats that would move the picture: a leak site listing, a statement from Mutual Ser, independent verification of samples, or evidence that buyers have taken the data. Until one of those appears, this stays a claim in a marketplace window.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Reach
1 independent groups, 1 updates, and 4 engagements.
Technical detail
The most concrete technical claim is that the data remains accessible without authentication, meaning no login would be required. That wording, if true, would suggest a live exposed endpoint rather than a single past download, though this rests entirely on the actor's word.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
The claimed contents mix corporate and personal data: tax IDs, phone numbers and addresses, historical financial transactions and payment records, personal information linked to financial histories, and supplier relationships with credit limits. Datasets are reportedly sold individually rather than as a single bundle.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Sources and evidence
This item rests on a single source: a post on X by DarkWebInformer, dated November 17, 2026, which includes a screenshot of the offer. The post is a secondary account relaying a threat actor's advertisement, not direct evidence of any breach.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Confidence is low by definition. Every material fact about the breach, the volumes and the exposure comes from the actor's claim as summarized by one monitoring account, and that account itself labels the claim unverified. Treat the numbers as an advertisement until samples or a victim statement appear.DarkWebInformerx.com · DarkWebInformer · xOpen original sourceSee in source list
Sources
- DarkWebInformerx.com · DarkWebInformer · x


